


Abstract
Strongly asymmetric public key agreement (SAPKA) is a class of key exchange between Alice and Bob that was introduced in 2011. The greatest difference from the standard PKA algorithms is that Bob constructs multiple public keys and Alice uses one of these to calculate her public key and her secret shared key. Therefore, the number of public keys and calculation rules for each key differ for each user. Although algorithms with high security and computational efficiency exist in this class, the relation between the parameters of SAPKA and its security and computational efficiency has not yet been fully clarified. Therefore, our main objective in this study was to classify the SAPKA algorithms according to their properties. By attempting algorithm attacks, we found that certain parameters are more strongly related to the security. On this basis, we constructed concrete algorithms and a new subclass of SAPKA, in which the responsibility of maintaining security is significantly more associated with the secret parameters of Bob than those of Alice. Moreover, we demonstrate 1. insufficient but necessary conditions for this subclass, 2. inclusion relations between the subclasses of SAPKA, and 3. concrete examples of this sub-class with reports of implementational experiments.
1. Introduction
Since Shannon proposed the concept of “perfect secrecy” in crypto-systems [1], in which he introduced a theoretically unbreakable system even against computational power, the distribution of secret keys between the sender (Alice) and receiver (Bob) via an insecure channel has been one of the greatest problems in cryptography.
The Diffie–Hellman (DH) public key agreement (PKA) protocol that was proposed in 1976 [2] and the Rivest–Shamir–Adleman (RSA) crypto-system that was presented in 1978 [3] represented the most significant works in the area of cryptography, and it was previously believed that the problem of key distribution had been resolved.
However, recent considerable developments in the computational power of eavesdroppers have introduced several potential (even if not immediate) threats against standard PKA algorithms and public key cryptographies, particularly for small key lengths [4]. To maintain security, users have been forced to select longer keys, and the increased key length has led to higher computational costs. Thus, the preparation of secure communication infrastructure, particularly for devices with limited memory and computational power, has become challenging. Furthermore, the threat of quantum computers that are currently under development and Shor’s algorithm [5] cannot be underestimated.
Considering the demand for algorithms that are resilient against any type of theoretical attack, including quantum algorithm-based attacks, the development and study of new PKA algorithms and public key cryptographies, namely post-quantum cryptography (PQC), has become widespread. PKAs and public key cryptographies based on lattice problems such as the shortest vector problem (SVP), closest vector problem, and learning with errors (LWE) are among the most well known methods. Among these, SVP-based PKA and public key cryptographies, including NTRU prime [6], NTRU-HRSS-KEM [7], and NTRU Encrypt [8], module LWE-based PKA such as CRYSTALS–Kyber [9], and ring LWE-based PKA including NewHope [10] are leading approaches in this research area and have been considered as candidates for the NIST (National Institute of Standards and Technology) standardization of PQC systems [11,12]. When the parameters are properly selected, the above algorithms are considered to be resilient against attacks that use quantum computers and sufficiently computationally efficient to be used in practice.
However, there has been substantial discussion regarding the security of such algorithms. For example, in certain LWE-based algorithms, even if sufficiently large parameters are selected, a possible weakness has been observed [13,14,15]. Moreover, the notion that the difficulty in solving ring LWE is equivalent to that of solving the LWE (the difficulty of LWE is discussed in [14,16]) has not yet been proven; thus, other cases of weakened security [9,10] may arise. Weak parameters for NTRU-type PKA algorithms and public key cryptography are also reported in [17]. Owing to these uncertainties in the parameter settings to maintain security even in an ideal situation (i.e., without assuming limited memory and computational power), the preparation of secure communication infrastructure with these new-generation algorithms for less capable devices has resulted in greater difficulty and insecurity. Although there is no doubt that these algorithms will offer significant benefits even after the post-quantum computer era, security analysis of these algorithms should continue until users can be provided with a “guide” that explains how to set parameters to ensure secure PKA and public key cryptography according to the needs and environments of users.
1.1. Research Concept and Goals
We define a function , which shows the computational costs for T calculation steps by a device with efficiency (calculation steps per time) as follows:
Thus, it is given by time (s, ms, or another unit). Let be a set of PKA algorithms and let be a function that shows the calculation steps required for Alice to calculate the bit length of the secret shared key (SSK) of an algorithm , which increases monotonically for N. denotes the calculation steps for Bob in a similar manner.
Next, we consider , which has the following relation:
for all . In this case, we suppose that the maximal computational cost that Bob is allowed to incur for the SSK calculation of , denoted by , is , which is achieved when the bit length of the SSK is some , and Bob can compute their SSK for all to satisfy:
where denotes the device efficiency of Bob. As is a monotonically increasing function for the bit size of the SSK, condition (2) is reduced to . Furthermore, if , where denotes the device efficiency of Alice, the SSK can be computed for all . Thus, Alice and Bob can calculate the SSK of a bit size that is equal to or less than within time .
For the same , we assume that and the maximal computational cost that Bob is allowed to incur is the same as (2), where is the smallest bit size of SSK to maintain security. Let Alice’s computational cost for calculating her SSK of bits be , and if Alice needs to calculate her SSK within the cost as well as Bob, the following relation must be satisfied:
where the equality holds for some , but in this case, must be satisfied because is a monotonically increasing function for the bit size of the SSK and . This observation indicates that they must either use an -bit SSK, which is obviously less secure than when using an -bit SSK, or let Alice incur a cost of , which is larger than . Most PKA algorithms, including the DH algorithm, satisfy (1), and there are many cases in which in modern society where IoT techniques are continually being developed; thus, this situation is inevitable in the near future, if not immediate.
We consider determining an algorithm denoted by , where
being satisfied for all is one solution to the above undesirable situation. We denote the maximal computational cost that Bob is allowed to incur as , which is defined as , where and it is the smallest bit size of SSK to maintain security. In addition to the above case, we suppose that both Bob and Alice must calculate her SSK within the maximal computational cost that Bob is allowed to incur . In this case, Alice can calculate all N bits of the SSK to satisfy
The equality holds when holds for some . In this case, it should be noted that is achieved; that is, Alice calculating the SSK of bits within time is possible, provided that
holds, which is impossible when (1), because in this case, the left-hand side is equal to 1, but the right-hand side is less than 1. As is given (we may say that is a communication environment in which the algorithm is used), (4) is not always achieved for some and . Conversely, we can determine the minimal environment where Alice and Bob can calculate bits SSK within time using by simply calculating the left-hand side of (4).
Based on the above considerations, our research goals are as follows:
- Constructions of .
- For , the determination of and for any .
- The construction of the PKA class to which belongs and the introduction of conditions for PKA algorithms to be members of this class.
As mentioned above, goal 2 provides a lower bound of to calculate the SSK of bits within time . Goal 3 provides instructions on how to construct PKA algorithms to possess the relation (3). Thus, improving algorithms such as those of [9,10] to possess this property may be possible by attempting to fix their parameters according to the class conditions. We do not attempt to improve these algorithms in this study, but this subject is worthy of consideration and will be one of our most important future works.
We consider that these goals are achievable by fully utilizing the characteristics of the PKA framework known as strongly asymmetric public key agreement (SAPKA) [18]. The characteristics, high level of generality, and asymmetry of the key agreement process of SAPKA are explained in Section 1.2, along with its definition, and concrete methods that are derived from the characteristics are explained in Section 2.
Note that this study is not focused on how to construct secure PKA algorithms against any types of theoretical attacks; rather, it investigates how to reduce Alice’s computational complexity while maintaining the security of one given PKA algorithm. Our main theorems (in Section 5) do not provide any instructions on how to enhance the security of PKA algorithms, and resilience against attack such as man-in-the-middle (MITM) attack is not discussed in this paper (we consider that these topics should be discussed after existence of is proven and mentioned in Section 7.1 ).
1.2. SAPKA Framework
We provide a brief definition of SAPKA (the explicit definition is presented in Section 2.4) and its characteristics in this section.
First, Bob prepares a multiplicative semi-group with 1. Subsequently, he selects five maps:
where must be an easily invertible map. In this case, “easily” means that the calculation of for all can be performed in polynomial time. Furthermore, , and must satisfy the following equation, which is known as the compatibility condition:
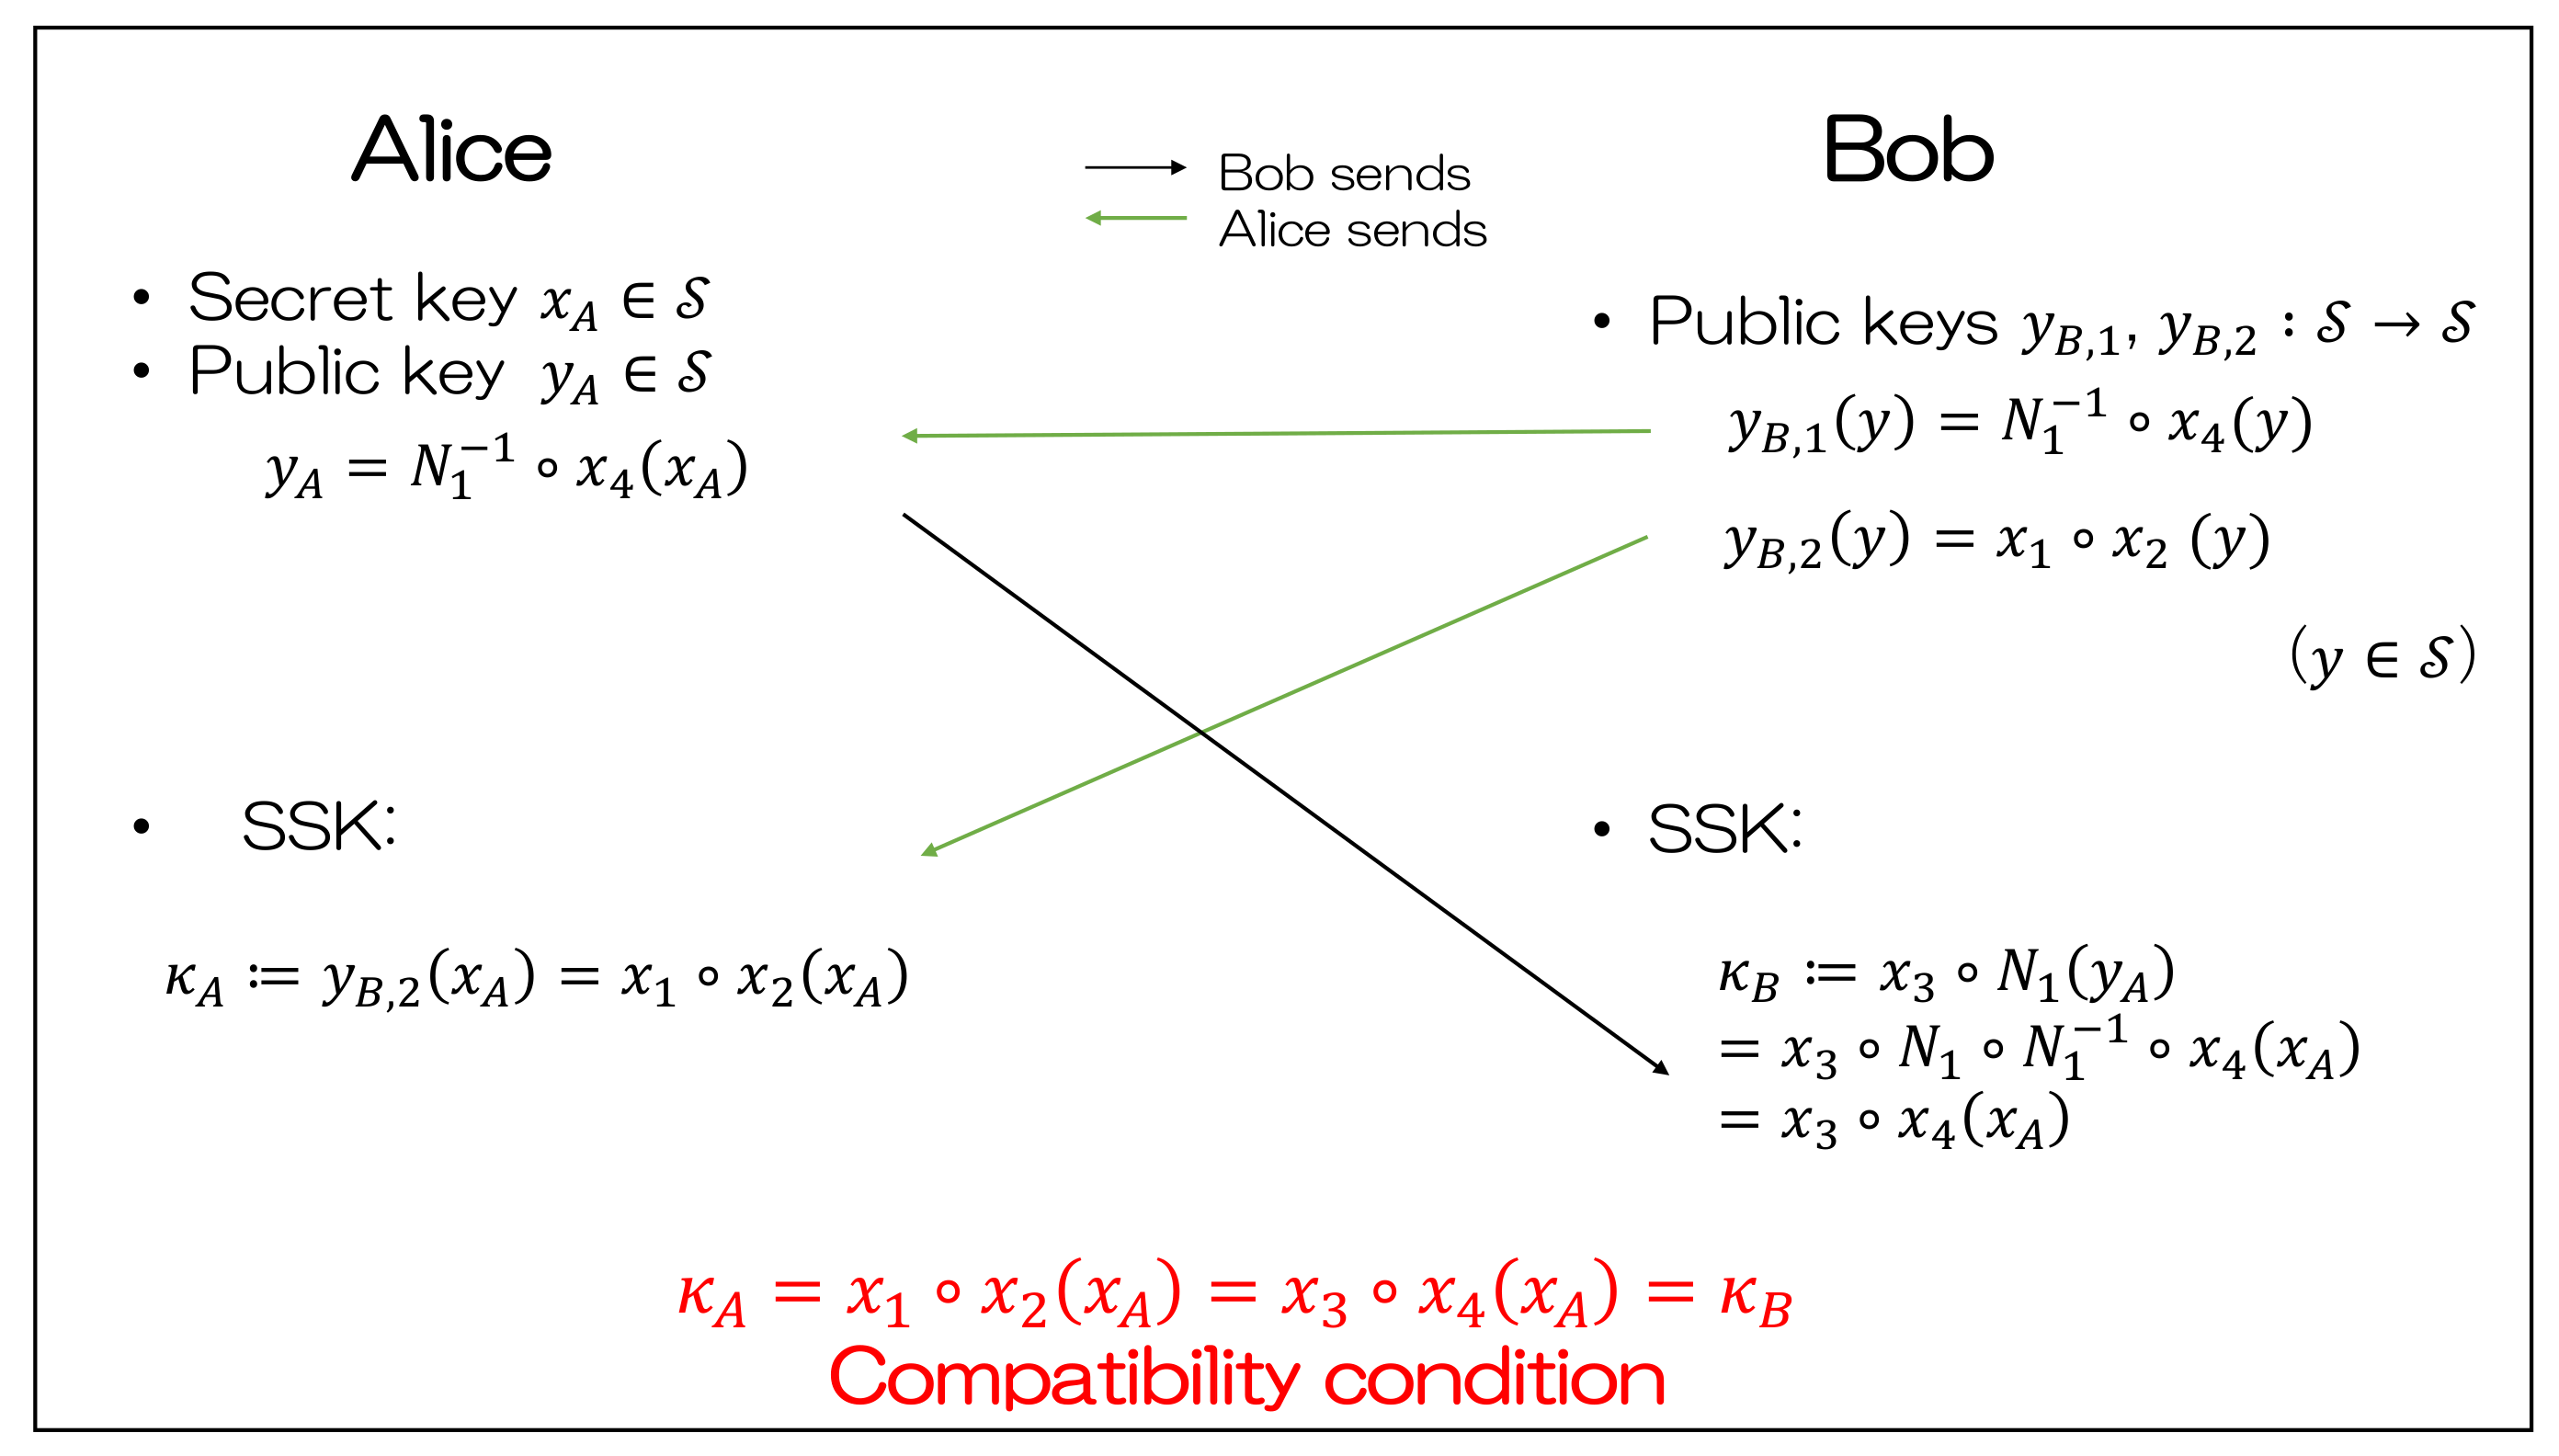
for all , where ∘ denotes the map composition. Equation (5) is a condition for Alice and Bob to calculate the same SSK (see the key agreement process in Figure 1). The key agreement process of SAPKA can be described as in Figure 1, and every secret/public key is displayed in Table 1.
Figure 1.
Key agreement process of SAPKA.
Table 1.
Complete list of key of SAPKA.
As can be observed from Figure 1 and Table 1, Bob’s public keys are described by the map compositions and not by the element of . Sending a map means sending the calculation rule of the map in combination with a set of parameters, which is the domain of the map. Thus, Alice simply follows the rules of and to calculate and , and to calculate these, she must first receive and from Bob. Regardless of the that Alice selects (provided that ), the equality of and holds, because the compatibility condition (5) holds for all elements of . The generality mentioned above arises from the fact that there are only several restrictions for the secret keys of Bob, namely , and semi-group . As the restrictions are only those in (5) and invertible regarding , Bob has substantial freedom in terms of the choices of these maps and the algebraic structure. By fixing these maps and concretely, various PKA algorithms can be described, including the most well known of these, namely the DH algorithm (presented in [18]). In this study, we do not attempt to describe new-generation algorithms such as [7,9,10] in the form of SAPKA. However, we are optimistic that these can be described because can be selected as not only scalars but also matrices, for example, with numerous options for .
Another notable characteristic of SAPKA is the asymmetry of the key agreement process. In this case, the asymmetry means that the number of public keys calculated by Alice and Bob differ, and thus, the two perform essentially different operations. Owing to this characteristic, an eavesdropper (Eve) must attempt attacks against a maximum of two public keys to obtain the secret information of either Bob or Alice. This may allow Alice to select her secret key from a set of small bit sizes and to reduce her computational complexity in certain cases. In Section 2, we explain Eve’s strategies for recovering the SSK from public keys, an observation from her strategies, and the research method derived from this observation.
2. Methods and Abstract of This Study
We explain the strategies for Eve to recover the SSK and the method for our research goal, which can be derived from the observation of her strategies.
2.1. Eve’s Strategies for Recovering SSK
Eve wishes to calculate or by determining the secret key of Alice or Bob from the public keys. She knows the two composed maps of Bob and one element of Alice, as follows:
- Eve’s Strategy 1
Subsequently, she can calculate
If is not an invertible map, she obtains a set instead of an element from (9). However, in this case, she can calculate the SSK as follows:
The second equation of (10) is obtained from the compatibility condition (5), and the final equation is obtained from the definition of (see Figure 1 or Step 5 of Section 2.4).
- Eve’s Strategy 2
First, Eve attempts to obtain a map from (6) and then attempts to obtain a map that satisfies
for all . Finally, she can calculate the SSK as follows:
Suppose that Bob constructs and to satisfy the following two requirements:
- Requirement 1.
- It is difficult to calculate for all in real time, or it is difficult to determine the invertible map of , in real time.
- Requirement 2.
- It is difficult to determine the map from in real time, or it is difficult to obtain a map to satisfy (11) in real time.
Then, it is difficult for Eve to obtain from (9) and to proceed to (12) in real time; that is, Eve cannot obtain the SSK in real time. It should be noted that the secret key that Alice selects is not strongly related to Eve’s breaking complexity owing to Requirement 1. This means that Bob may take substantially more responsibility for maintaining security than Alice. In this case, Alice can select her secret key space as a small one in terms of the bit size, provided that an exhaustive search for is difficult in real time, and we expect that this will reduce Alice’s computational complexity for and .
2.2. Methods
According to this observation, the methods that can be established for the research goal can be derived as follows:
- Introduce algorithms from SAPKA (Section 3).
- Estimate the breaking complexity of these algorithms under the assumption that the secret key space of Alice is smaller than that of Bob and verify whether or not Alice’s small key space reduces the breaking complexity of the algorithms (Section 4.2 and Section 4.3).
- For algorithms for which Alice’s small key space does not reduce the breaking complexity, estimate their computational complexity to calculate the keys of both Alice and Bob (Section 4.4 and Section 4.5).
- Construct the SAPKA subclass for which the algorithms possess the relation that the complexity of Alice for her keys is smaller than that of Bob (we call this subclass the “main SAPKA subclass” until we give definition of it) and introduce the necessary conditions for the subclass by generalizing the results of 3 (Section 5.1 and Section 5.2).
In Section 6, we implement some of the algorithms in Section 3 and report the experimental results. We can concretely observe what can be offered by the algorithms of the subclass constructed in Section 5.1.
At the beginning of Section 5, we add restrictions to the SAPKA framework, particularly for the public keys of Bob, before discussing our main themes. We explain these restrictions briefly below.
2.3. Restrictions on SAPKA Framework
We have already explained the high level of generality of SAPKA. However, owing to this generality, algorithms that do not ensure secure PKA are also included in this class. We present one example as follows:
Let be for some prime number p. Bob selects the numbers and keeps them secret. Let the maps be defined, for , as:
- .
In this case, all keys are described as in Table 2.
Table 2.
Complete list of key of example algorithm of SAPKA.
The SSK calculations are performed as follows:
In this case, Bob sending means that must be a public key, although this element is supposed to be a secret; otherwise, Alice cannot calculate . Eve can easily calculate Alice’s secret key with ; thus, Eve can recover the SSK by calculating . Without limiting this type of algorithm to be included in the SAPKA class, the main subclass that we attempt to construct in Section 5 can include weak algorithms. In this case, the subclass cannot be the one that we aim to construct.
To limit algorithms such as the above example, we add restrictions on the construction of Bob’s public keys using a map referred to as a “non-easily invertible map” with the following definition.
Definition 1.
The mapis called as a non-easily invertible map if the calculationfor allis difficult to compute in the mean of the computational complexity, and the order of complexity for computingis equal to or greater than, where n is the bit size of y andis a monotonically increasing function:
for some.
O of this definition is Landau’s big-O notation (Definition 5 in Section 4.1). We limit Bob’s public keys and to be constructed as
for certain non-easily mapped and certain maps . By doing so, attacks from Eve cannot be performed within a polynomial time. Furthermore, with several additional restrictions in Section 5, Requirement 2 of Section 2.1 can be achieved.
We attempt 4. of the method mentioned in Section 2.2 within this restricted SAPKA class with a non-easily invertible map (the explicit definition of this restricted SAPKA class by a non-easily invertible map is also provided Section 5).
2.4. Explicit Definition of SAPKA
We present the definition of SAPKA [18]. The SAPKA algorithms have the following common ingredients:
- a multiplicative semi-group S with 1;
- a set of easily invertible maps , known as noise space; and
- a set of maps .
In the above, S is public, and and belong to Bob’s secret. From the key space,
Bob prepares the quintuple as their secret key, and must satisfy the following condition, which allows Alice and Bob to obtain the SSK.
Definition 2.
Letbe a multiplicative semi-group with 1. If the functionssatisfy the following condition for all:
the mapsare said to be compatible, where ∘ denotes a map composition.
Definition 3.
For a multiplicative semi-groupwith 1 and the quintuple, if the mapssatisfy (13), we state that C is a member of the SAPKA class. We express this relation as:
The key agreement process of SAPKA is described as follows:
- Step 1B
- Bob prepares the maps , of which satisfy (13).In this case, each of is their secret key.
- Step 2B
- Bob constructs their public keys as a map for each:and sends to Alice.
- Step 1A
- Alice selects her secret key from .
- Step 2A
- Alice calculates her public key as follows:and sends it to Bob.
- Step 3A
- Alice calculates the SSK denoted by as follows:
- Step 3B
- Bob calculates the SSK denoted by as follows:
2.5. Abstract of This Study
Here, we give an outline of this study, including research goal, short abstract of each section.
- Research Goal
Construction of algorithms that possess the property that Alice’s complexity for SSK is smaller than that of Bob’s and introduction of SAPKA subclass that includes algorithms of the same property.
- Section 3: Concrete Examples of SAPKA
We show concrete examples that how Alice and Bob calculate the SSK, respectively, when the key agreement process is asymmetric. Three examples that are normal DH of SAPKA description, noise element included type DH, and matrix type DH are shown.
- Section 4: Breaking Complexity of SAPKA Algorithms
In this section, we demonstrate what problems that the algorithms of Section 3 are reduced to. Estimations of breaking complexities are done under the assumption that Alice’s secret key space is smaller than Bob’s secret key space. Here, we can see how problems algorithms reduced to are varied according to algebraic structure and SAPKA parameters. Finally, using some of SAPKA algorithms, we discuss how small Alice’s secret key space can be while maintaining security.
- Section 5: Generalization
Here, we try to construct the SAPKA subclass of property that Alice’s computational complexity for SSK is smaller than that of Bob. At first, we exclude algorithms of weak security from the subclass framework as we mentioned in Section 2.3. Without this procedure, the subclass can contain algorithms of above property but sufficiently weak security so that Eve can obtain the SSK within polynomial time. After this limitation is done, we define the subclass and introducing some conditions (only necessarily conditions for algorithms into the subclass) by expanding the results of Section 4 so that it can be applied to the SAPKA framework.
3. Concrete Examples of SAPKA
3.1. DH
As demonstrated in [18], the SAPKA class includes the DH algorithm. However, the process is symmetric because, in this case, , where p is a prime number (thus, forms a finite field), is the public parameter, is the identity map, and Alice can calculate the public key , even before receiving . The process is asymmetric in the sense that Alice and Bob use different secret information, but it is symmetric in the sense that the two perform the same operations independently.
3.2. Noised DH (NDH)
The following example is a variant of the DH that does not improve its security substantially but is useful to illustrate the concept of SAPKA algorithms simply.
The components are the same as those in Section 3.1. Bob selects their secret keys . The key agreement process of the NDH algorithm is described by the following steps.
- Step 1B
- Bob prepares the quintuple as follows:
- ,
where y is selected arbitrarily from . - Step 2B
- Bob constructs their public keys as a map for eachand sends to Alice. This is equivalent to sending .
- Step 1A
- Alice selects her secret key from .
- Step 2A
- Alice calculates her public key as follows,and sends it to Bob.
- Step 3A
- Alice calculates the SSK denoted by as in the DH case:
- Step 3B
- Bob calculates the SSK denoted by as follows:
3.3. Schur Exponentiation-Based DH (SEDH)
Let be the multiplicative semi-group of matrices with entries in . The algorithm introduced in this section uses Schur exponentiation; that is, element-wise matrix exponentiation. The symbol is defined as follows:
The key agreement process is as follows:
- Step 1B
- Bob selects a matrix , an invertible matrix , and a primitive element g of . Subsequently, he constructs the quintuple for all as follows:
- ,
where . The compatibility condition holds for all and : - Step 2B
- Bob constructs their public keys as a map for eachfor all . In this case, can also be expressed as follows:Bob sends the maps to Alice. This is equivalent to sending the matrices .
- Step 1A
- Alice selects her secret key .
- Step 2A
- Alice calculates her public key for all as follows:and sends it to Bob.
- Step 3A
- Alice calculates the SSK denoted by for all as follows:
- Step 3B
- Bob calculates the SSK denoted by for all as follows:
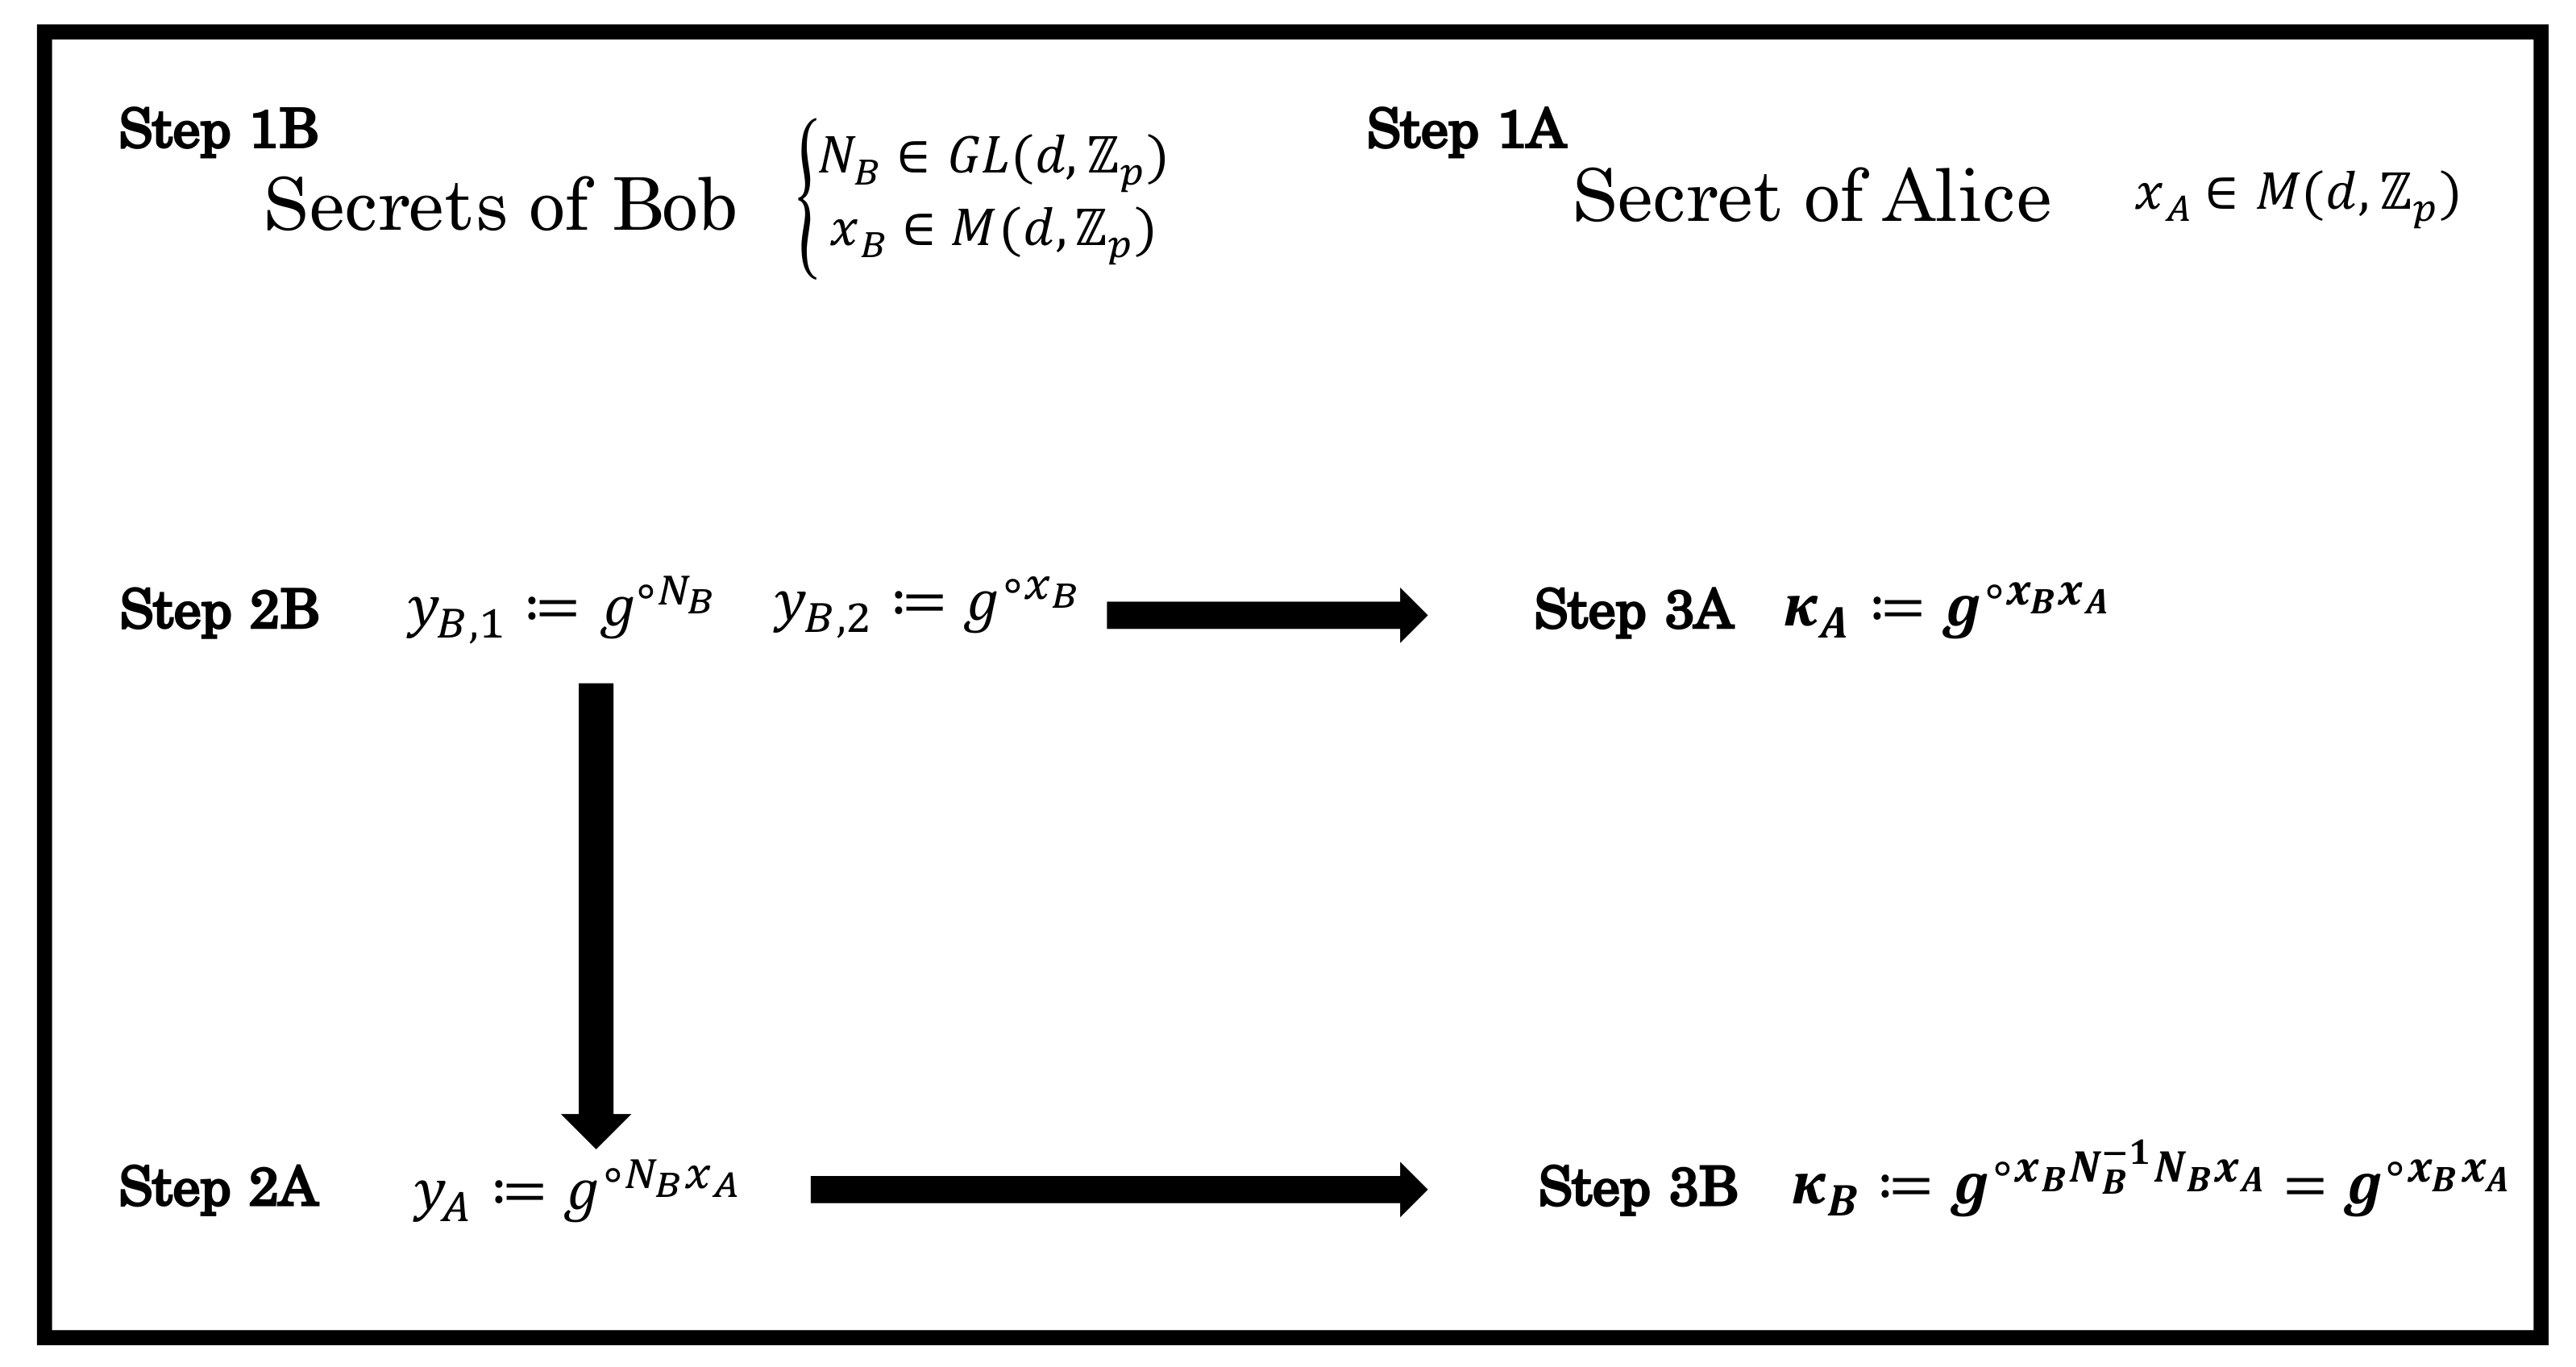
This process is illustrated in Figure 2.
Figure 2.
Key agreement process of Schur exponentiation-based DH.
Remark 1.
Let be a vector space of . Each of the above maps can also be considered as the map and the condition
is satisfied for all and , where are the same as above. Thus, Alice can select her secret key from and the computational complexity for calculating , , and is obviously reduced compared with the case when . The precise breaking and computational complexities for the of both the and cases are investigated in the following section.
4. Breaking Complexity of SAPKA Algorithms
As mentioned in Section 2.2, we estimate the breaking complexity (Section 4.2 and Section 4.3) and computational complexity (Section 4.4) of the algorithms in Section 3.2 and Section 3.3 under the assumption in Section 4.1.
4.1. Assumptions
Let n and m be numbers in , and . We define two functions and , which represent the bit lengths of the input. The difference between the two functions is the domains. The input of the first one is from , and the second one is from . The semi-groups of the above two algorithms are constructed based on a prime number p, where . In this case, we can express the bit size of the element in as when and when . We construct subsets denoted by of for both the and cases, respectively, as follows:
with the aim of determining whether the complexity of the algorithms in Section 3.2 and Section 3.3 are reduced if we suppose that Alice’s secret key is selected from the small bit length set .
Prior to investigating the breaking complexity of the algorithms in Section 3.2 and Section 3.3 under the assumption and a certain condition for n and m, we demonstrate that not only the complexity, but also the order of complexity (a definition of order is provided in Definition 5) to compute one discrete logarithm problem (DLP) differ between the cases when an exponent is selected from a larger bit length set and from a smaller bit length set.
The required settings are as follows:
- a prime number p, where ;
- a semi-group ;
- a subset ; and
- a map , , where g is a primitive element of .
We prove that if for some monotonically increasing function of not a linear and monic polynomial, the calculation of the DLP, namely
is easier when than when in terms of the complexity and order (Proposition 1). First, we name this input y of according to the size of set y as per the following definition:
Definition 4.
Let n and m be numbers in , and let n be the bit size of each element of . For a given map , defined as
where g is an element in , if the set y belongs to , we call this y anm-bit logarithm. If the set is , y is known as ann-bit logarithm.
The complexity of obtaining the n-bit logarithm refers to the complexity of calculating when (for the m-bit logarithm, ).
We represent the time complexity using the function , where the input is the bit size and the output is the multiplication steps. The complexity of calculating the DLP of the m-bit logarithm is given by [19,20]. In this case, the complexity of calculating the n-bit logarithm is . Obviously, when ; however, we should also consider how the complexity increases as m increases. We can compare the growth rate of and using Landau’s big-O notation with the following definition:
Definition 5.
For functions , if there exist such that
is satisfied for all , we state that has an order of time complexity, and we describe it as
Relation (19) indicates that is a set defined by:
Therefore, for two complexity functions , where for all and , , if we wish to state that the growth rate of is higher than that of T (the order of is higher than T), we can simply describe it as follows:
or
for all m. In this case,
hold. We can prove that the growth rate of is higher than as follows:
Proposition 1.
If and only if the monotonically increasing functionfor satisfyingis a not linear and monic polynomial, the growth rate ofis higher than; that is,
holds.
Proof.
Note that and . Suppose that s is a one-degree but non-monic polynomial defined as:
where , . If holds in this case, there must exist the constants such that for all ,
is satisfied. However, in this case, holds, so that c cannot be a constant. Thus, in this case,
holds. When the case s is over a one-degree polynomial, it is obvious that there is no to satisfy (20) for all .
If s is a linear and monic polynomial described as
where , we have
□
Therefore, if Alice and Bob attempt a key exchange using the DH algorithm, where Bob’s secret key is
and Alice’s secret key is
Eve should attempt to obtain , which is easier for her to obtain than . The security of the algorithms in Section 3.2 and Section 3.3 also depends on the difficulty of the DLP, but these algorithms may not be the same as DH owing to one of Bob’s public keys and especially the map . In Section 2.1, we discussed the requirement for to allow Alice to select her secret key from a small bit length set without reducing the breaking complexity. For both algorithms, Requirement 2 is satisfied if Bob selects , as it is an n-bit logarithm for with the algorithm of Section 3.2, and similarly, is selected with the algorithm of Section 3.3. Of course, in this case, the number n must be sufficiently large to ensure that the calculation of the n-bit logarithm is not achieved in real time.
At this point, we focus on verifying whether the other algorithms in Section 3.2 and Section 3.3 satisfy Requirement 1. of Section 2.1. Subsequently, we attempt to determine the polynomial s; that is, how small m can be and the computational complexity of these algorithms for each key of Alice and Bob when m is selected to be as small as possible (Section 4.4).
4.2. Eve Attempts an Attack against NDH
We assume the following:
- a prime number p, where ;
- a semi-group ;
- a subset ;
- ;
- ;
- a map , , where g is a primitive element of ;
- a non-linear and monic polynomial s, where for all .
Eve’s goal is to obtain from the following public keys
- ,
and public elements
- .
She must calculate
As she does not know , it appears that she must obtain the n-bit logarithm by calculating before obtaining the m-bit logarithm . However, (21) can be described as
Thus, when we define a map such that
, we can construct using only , which is public. For this attack, Eve only needs to calculate to obtain the m-bit logarithm . Therefore, it can be said that Alice selecting a small bit length set reduces the breaking complexity for Eve; that is, Requirement 1 of Section 2.1 is not satisfied in this case.
4.3. Eve Attempts an Attack against SEDH
We assume the following:
- a prime number p, where ;
- a semi-group ;
- a subset ;
- ;
- ;
- a map , , where g is a primitive element of ; and
- a not linear monic polynomial s, where for all .
Eve’s goal is to obtain from the following public keys:
- ,
where , and the following elements:
- ,
to calculate
for all . It appears that she first needs to obtain an element by calculating for all , the complexity of which is equivalent to the complexity for calculating n-bit logarithms for the map , because she does not know , so as to obtain . After obtaining , she can proceed to the final two equalities of (22), and the complexity of calculating for all is equivalent to the complexity of calculating m-bit logarithms for the map . We now verify that Eve really needs to calculate at least the same amount as to obtain n-bit logarithms by calculating for all . In Attack 1, we attempt to find other descriptions for map , as in Section 4.2. In Attack 2, we attempt an attack in which Eve avoids calculating DLPs for , and we compare the breaking complexity of the attack with an exhaustive search for . In Attack 3, we attempt to determine the least complexity that Eve requires to obtain . Hereafter, we refer to the logarithm of matrix as follows:
- Attack 1
Using the known element , Eve attempts the following calculation for all :
In this case, X holds for the relation
where • denotes element-wise matrix multiplication. Obviously, does not always hold, so also does not hold. Moreover, to obtain , Eve needs to calculate .
- Attack 2
We introduce an attack in which Eve does not calculate . The public key of Alice is described as
- Step 1
- For row of , Eve creates a matrix to satisfy
- Step 2
- For all , Eve calculates
- Step 3
- For all , Eve verifies whether or notis true.
- Step 4
- If (26) is true for all , Eve can recover row of :
In Step 2, Eve needs to calculate at least two DLPs of m-bit logarithms; thus, she requires multiplications. As forms a group under multiplication, for any arbitrary element e in , there exists a unique such that:
for each . Thus, Eve has choices for and each , and therefore, Eve must repeat Steps 2 to 4 at most times. The total multiplications required for this attack is denoted as:
which is much larger than the total multiplications required for an exhaustive search on each row of , namely:
- Attack 3
Suppose that Eve attempts to determine directly from the formula of Alice’s public key :
As is an invertible matrix, this is equivalent to solving the following system for :
for all and given , . The least complexity for finding X from (28) is expressed by the following theorem:
Theorem 1.
The complexity of solving (28) for is equal to or greater than the complexity of obtaining from .
Proof.
Suppose that Eve can determine from (28) for a given and with a complexity denoted by the function defined as , where p is a polynomial. Under this assumption, Eve can solve system (28) even when (thus, ) because, in this case, the complexity is , which is also a polynomial. It should be noted that solving (28) is equivalent to solving the following system for all :
for given matrices , , where t denotes matrix transposition, because
for all . This emphasizes that Eve can solve the system of both variable matrices by left multiplication and right multiplication on the Schur exponent of a given matrix. Therefore, once she has obtained and calculates within polynomial time, the following system can also be solved for an unknown :
for all within polynomial time. As is the matrix logarithm of , we can state that, if Eve can solve system (28) for X within polynomial time, she can obtain n-bit logarithms within polynomial time. □
This theorem claims that the problem of calculating is polynomial-time-reducible to the problem of solving system (28) for .
4.4. Determination of n and m
We investigate how large the bit sizes n and m must be, as well as the computational complexity of calculating the public keys and SSK for Alice and Bob according to n and m. If the attacks on SEDH are only those in Section 4.3, Eve must execute an exhaustive search for each row of (as the attack is performed by each row, Eve requires d times exhaustive searches within a vector space of size ) or must obtain , the difficulty of which is equivalent to obtaining n-bit logarithms, as in the above attacks. We assume that attacks against SEDH are only those described in Section 4.3, and we determine the sizes of n and m. Considering that the difficulty for Eve to obtain depends on the difficulty of the DLP and that of obtaining directly from (24) by an exhaustive search depends on the vector space of size , n and m must satisfy the requirements in Table 3.
Table 3.
Requirements for n and m.
As mentioned in Section 4, the complexity of one n-bit logarithm denoted by the function
is , and the complexity of an exhaustive search for of each row denoted by the function is . (In fact, Eve must solve DLPs or d exhaustive searches for a vector space , but and d are so trivial for exponential functions that we consider these complexities for only one number.) If Alice and Bob would like the breaking complexity for one DLP and that for an exhaustive search for one row of to be equalized, the polynomial mentioned at the beginning of Section 4.3; that is, the relation between n and m, is obtained by the following theorem:
Theorem 2.
If the time complexity for obtaining one n-bit logarithm is equal to the complexity of an exhaustive search within a vector space of size, the polynomial for is obtained by
Proof.
We obtain
□
With this relation, what does the computational complexity for Alice and Bob become?
4.5. Computational Complexity of SEDH for Alice and Bob
For a given , approximately multiplications are required if the bit size of the exponent is n to calculate one scalar exponentiation. Furthermore, approximately m multiplications are required if the bit size of the exponent is m. Thus, the calculation
requires approximately multiplications if . If , it requires approximately multiplications. Moreover, the calculation
requires multiplications if and multiplications if for each . Thus, according to (14) and (15), the computational complexities required by Alice for and her SSK denoted by the functions of m are
From the calculations of , , and (16), Bob’s computational complexities for , , and their SSK, denoted by the functions of n, become
As , , , and can be described as functions of m as follows:
Thus, the total complexity for Alice and Bob can be compared:
When d is given, and have the same order of complexity. and are considered as coefficients.
Of course, we can consider the total complexity for Alice and Bob by the functions of d, which are defined as
for a given m. In this case, , , and are obvious. Which values of m and d should be given and which should be the input of the functions can be determined the environment in which the algorithm is used, such as the computational resources and communication infrastructure.
Remark 2.
As mentioned in Remark 1, Alice can select her secret keynot only as a matrix, but also as a vector, whereas and are selected as matrices. Let be a vector space of , where and a subset of , and suppose that is selected from . In this case, the breaking strategy against this algorithm for Eve is as follows:
- solvingDLPs forand d DLPs for, and
- an exhaustive attack forwithin, the size of which is.
That is, the breaking complexity is equivalent to the case whenin terms of the order of complexity. Thus, there is also no problem in selecting n and m from the relation of Theorem 2 in this case. The computational complexities for, , and , which are denoted by the functions, and, are
for a given d. It can be observed that the complexities are reduced from (34), (35), and (38). Moreover, the calculation of (33) is independent for each element , and thus, it can be computed in parallel. The calculation is also parallelized for each . In Section 6, we report the results of the implementational experiments of SEDH in the case of . To determine how rapidly the calculation is performed, particularly for Alice, we compare the calculation speed with that of the usual DH algorithm.
5. Generalization
In this section, all investigations are conducted under the following assumptions:
- the numbers and a not linear and monic polynomial s, where for all ;
- a number p, where ;
- a semi-group , where ;
- a subset ; and
- .
In the above, is the same notation as that in Section 4.1. Furthermore, the constant k is uniquely determined by the properties of , such as the dimensions of the matrices and vectors. For example, when and when .
As mentioned in Section 2.3, we first construct a SAPKA subclass, in which the security of each algorithm is ensured by a non-easily invertible map (Definition 1). Thereafter, we attempt to construct the main SAPKA subclass mentioned in Section 2.2. We introduce inclusion relations between other subclasses and necessary conditions for algorithms to belong to the main subclass in Section 5.2.
We present the definition of the subclass based on the non-easily invertible map.
Definition 6.
For a multiplicative semi-group and the quintuple , where the maps satisfy (13) and is an easily invertible map of , if maps exist, where is easily invertible and a non-easily invertible map exists such that the following equations:
are satisfied for all , where e is an identity element of , the quintuple C is a member of the class, and we express this relation as
From (40) and (41), and the compatibility condition of (13), the equation
for all is automatically satisfied. Using (42), the equation
holds for all . Thus, the public keys and SSK of Alice and Bob for the algorithms in this class can be described as Table 4.
Table 4.
Public keys and SSK of Alice and Bob for class.
Moreover, (41) and (42) ensure that the maps and and thus the element , cannot be disclosed by Eve within polynomial time. If and , the complexities for calculating
are reduced compared to the case when (43) holds (see Remark 3 in Section 5.1). If are linear maps, for example, Eve can obtain a linear map to satisfy:
by matrix multiplication, because is described as a matrix. Moreover, as is a multiplicative semi-group, for any can be expressed as and either of the equations
or
holds for all . Thus, only if Eve knows the calculation rule of map can she obtain a map to satisfy
for all . Finally, she can calculate the SSK as follows:
Of course, if the maps are not linear, this attack may be impossible, but if (43) holds and n is sufficiently large to make the calculation of difficult in real time, Eve cannot proceed to (46). Thus, Requirement 2 of Section 2.1 is achieved for all algorithms in the class.
- Algorithms of Class
It can be proven that in Section 3.2 and in Section 3.3 belong to the class. For , if and Bob defines as
- ,
then (40) holds, and (41) and (42) are satisfied according to the descriptions of the public keys of Bob in Table 5.
Table 5.
Public keys of Bob for .
For , if and Bob defines as
- ,
Table 6.
Public keys of Bob for .
At this point, we construct a subclass, the algorithms of which possess the same property as the SEDH that was investigated in Section 4.3 and Section 4.4, namely biased computational complexity to Bob (see Section 5.1). We mainly focus on this class in this study.
5.1. Notations and Definitions
Prior to constructing the main subclass (Definition 9), we present several definitions and notations below. Definition 7 provides one subclass in which the algorithms are symmetric and include DH. In Section 5.2, we investigate how this subclass relates to the main subclass of Definition 9. Definition 8 provides the name for the input y of a given map according to the set of y. We use this definition to emphasize the difference in complexity for calculating of a given map when and when . The notations directly below Definition 8 are functions that demonstrate the complexity for calculating each key. As these notations and Definition 8 allow us to express the breaking and computational complexity for each key quantitatively, the main subclass can be defined by equalities and inequalities.
Definition 7.
For the quintuple C such that , if , we state that C is a member of the symmetric class, and we express this relation as
If , one of the public keys of Bob is described as
where . This means that Bob sending is equivalent to simply informing Alice of the construction rule of . Alice can calculate without any secret/public information from Bob. Symmetry means that the number of public keys that both Alice and Bob construct is essentially one, and they can construct their public keys without any public/secret information from the other.
For in Section 3.2, if the parameter is equal to 1, describes the usual DH. We denote this case of as , and we obtain
Moreover, in the case of , denoted by , is
Definition 8.
For a given non-easily invertible map , if the set to which the input y belongs is , we refer to the input y as a-bit element. If the set to which the input y belongs is , we refer to the input y as a-bit element
The complexity of obtaining the -bit element means the complexity of calculating when (for the -bit element, ).
We define the following functions of bit size that demonstrate the complexity of calculating each public key and SSK as well as the complexity for Eve to obtain a certain key:
- : the complexity required for Bob to construct ;
- : the complexity required for Bob to construct ;
- : the complexity required for Alice to calculate ;
- : the complexity required for Alice to calculate her SSK ;
- : the complexity required for Bob to calculate their SSK ;
- : the least complexity required for Eve to obtain Alice’s secret key from public informations, where the input of is m; and
- : the complexity required to compute for map , where the input of is m if and n if .
Furthermore, for , we define the following functions to describe their order:
- to obtain the relation , and
- to obtain the relation .
Example 1.
- If , , and are defined as functions of n, and are defined as functions of m, and the polynomial s is concretely determined, we can compare the total computational complexity for Alice and Bob as per Section 4.5.
- The least complexity for Eve to obtain in Section 3.3 is determined as
- The complexity of obtaining the -bit element, where is the non-easily invertible map of as defined in Table 6, is expressed as
- The complexity of obtaining the -bit element is determined as
In general, the complexity of obtaining the -bit element for a given non-easily invertible map is described by , and that of the -bit element is . We can compare not only the complexity but also the order of complexity of the two using the map defined above, as per the following Remark 3.
Remark 3.
When the order of complexity for computing the -bit element for map is equal to , where :
holds, and the equality holds if and only if s is a linear monic polynomial for some :
This can be proven in a similar manner to Proposition 1, and in this case, s is restricted as a non-linear and monic polynomial, so the equality never holds.
When the order of complexity for computing the -bit element is greater than , although the sufficient and necessary condition of s for the equality of (47) may not be the same,
holds because, for all m, the ratio is much larger and cannot be a constant in this case. This means that when s is a not linear and monic polynomial, the problem of obtaining the -bit element by computing and the problem of obtaining the -bit element by computing belong to different orders of complexity classes. Furthermore, needless to say, holds.
Definition 9.
For the quintuple C of , if the following relations hold:
we state that C is a member of the class that is computationally biased to Bob , and we write this relation as
If the relation
holds, C is a member of the computationally unbiased class, and we write this relation as
Relation (49) indicates that the breaking complexity of an algorithm that is constructed from is equal to or greater than the complexity that is required to obtain the -bit element, even if is selected from . Furthermore, (51) indicates that when , the breaking complexity is equal to or less than that of obtaining the -bit element. As noted in Remark 3, not only does hold, but the orders of complexity are also different, so there cannot exist a such that . Thus, we obtain Lemma 1 in Section 5.2.
5.2. Inclusion Relations between Subclasses of SAPKA and Necessity Condition
Lemma 1.
For and , the following relation holds:
According to the attack introduced in Section 4.3, we obtain the following results.
Theorem 3.
For in Section 3.3, if Attack 2 of Section 4.3 and the exhaustive attack for are only attacks without calculating or there exist other attacks but the order of complexity is equal to or greater than ,
Proof.
According to Attack 3 in Section 4.3 and the descriptions of and in Example 1, we obtain
Under this assumption, holds, and thus, we obtain
from Section 4.5. □
We introduce two necessary conditions for the class.
Theorem 4
(Necessary Condition 1). If the quintuple , the relation
holds.
Proof.
We prove the contrapositive. If , Alice’s public key is described as:
according to (40), but and are identities; thus, becomes
Because , is a -bit element for map , and we obtain
Thus, . Moreover, Lemma 1 indicates that . □
Corollary 1.
Theorem 5
(Necessary Condition 2). If the quintuple , then there does’t exist a map such that to satisfy
for all , .
Proof.
We prove the contrapositive. We assume that for , there exists a map to satisfy
for all . According to (54), can be described as
This indicates that is a -bit element for a map . In combination with (55), the relation
holds. Thus, ; that is, is proven. □
Corollary 2.
Proof.
Remark 4.
Theorem 1 of Section 4.3 implies that there does not exist a map to satisfy with as for algorithm of .
According to the proof of Theorem 4 and Corollary 2, we obtain the following inclusion relation:
Corollary 3.
Proof.
From the proof of Theorem 4,
is obtained. Thus, we obtain
Moreover, is related to , but according to Corollary 2. Thus, is obtained. □
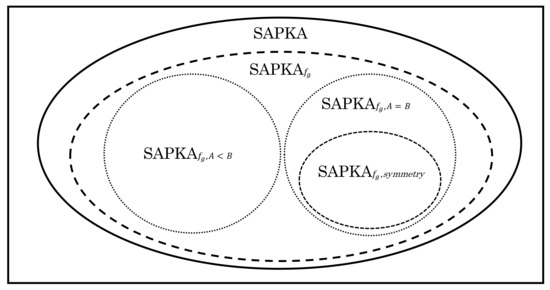
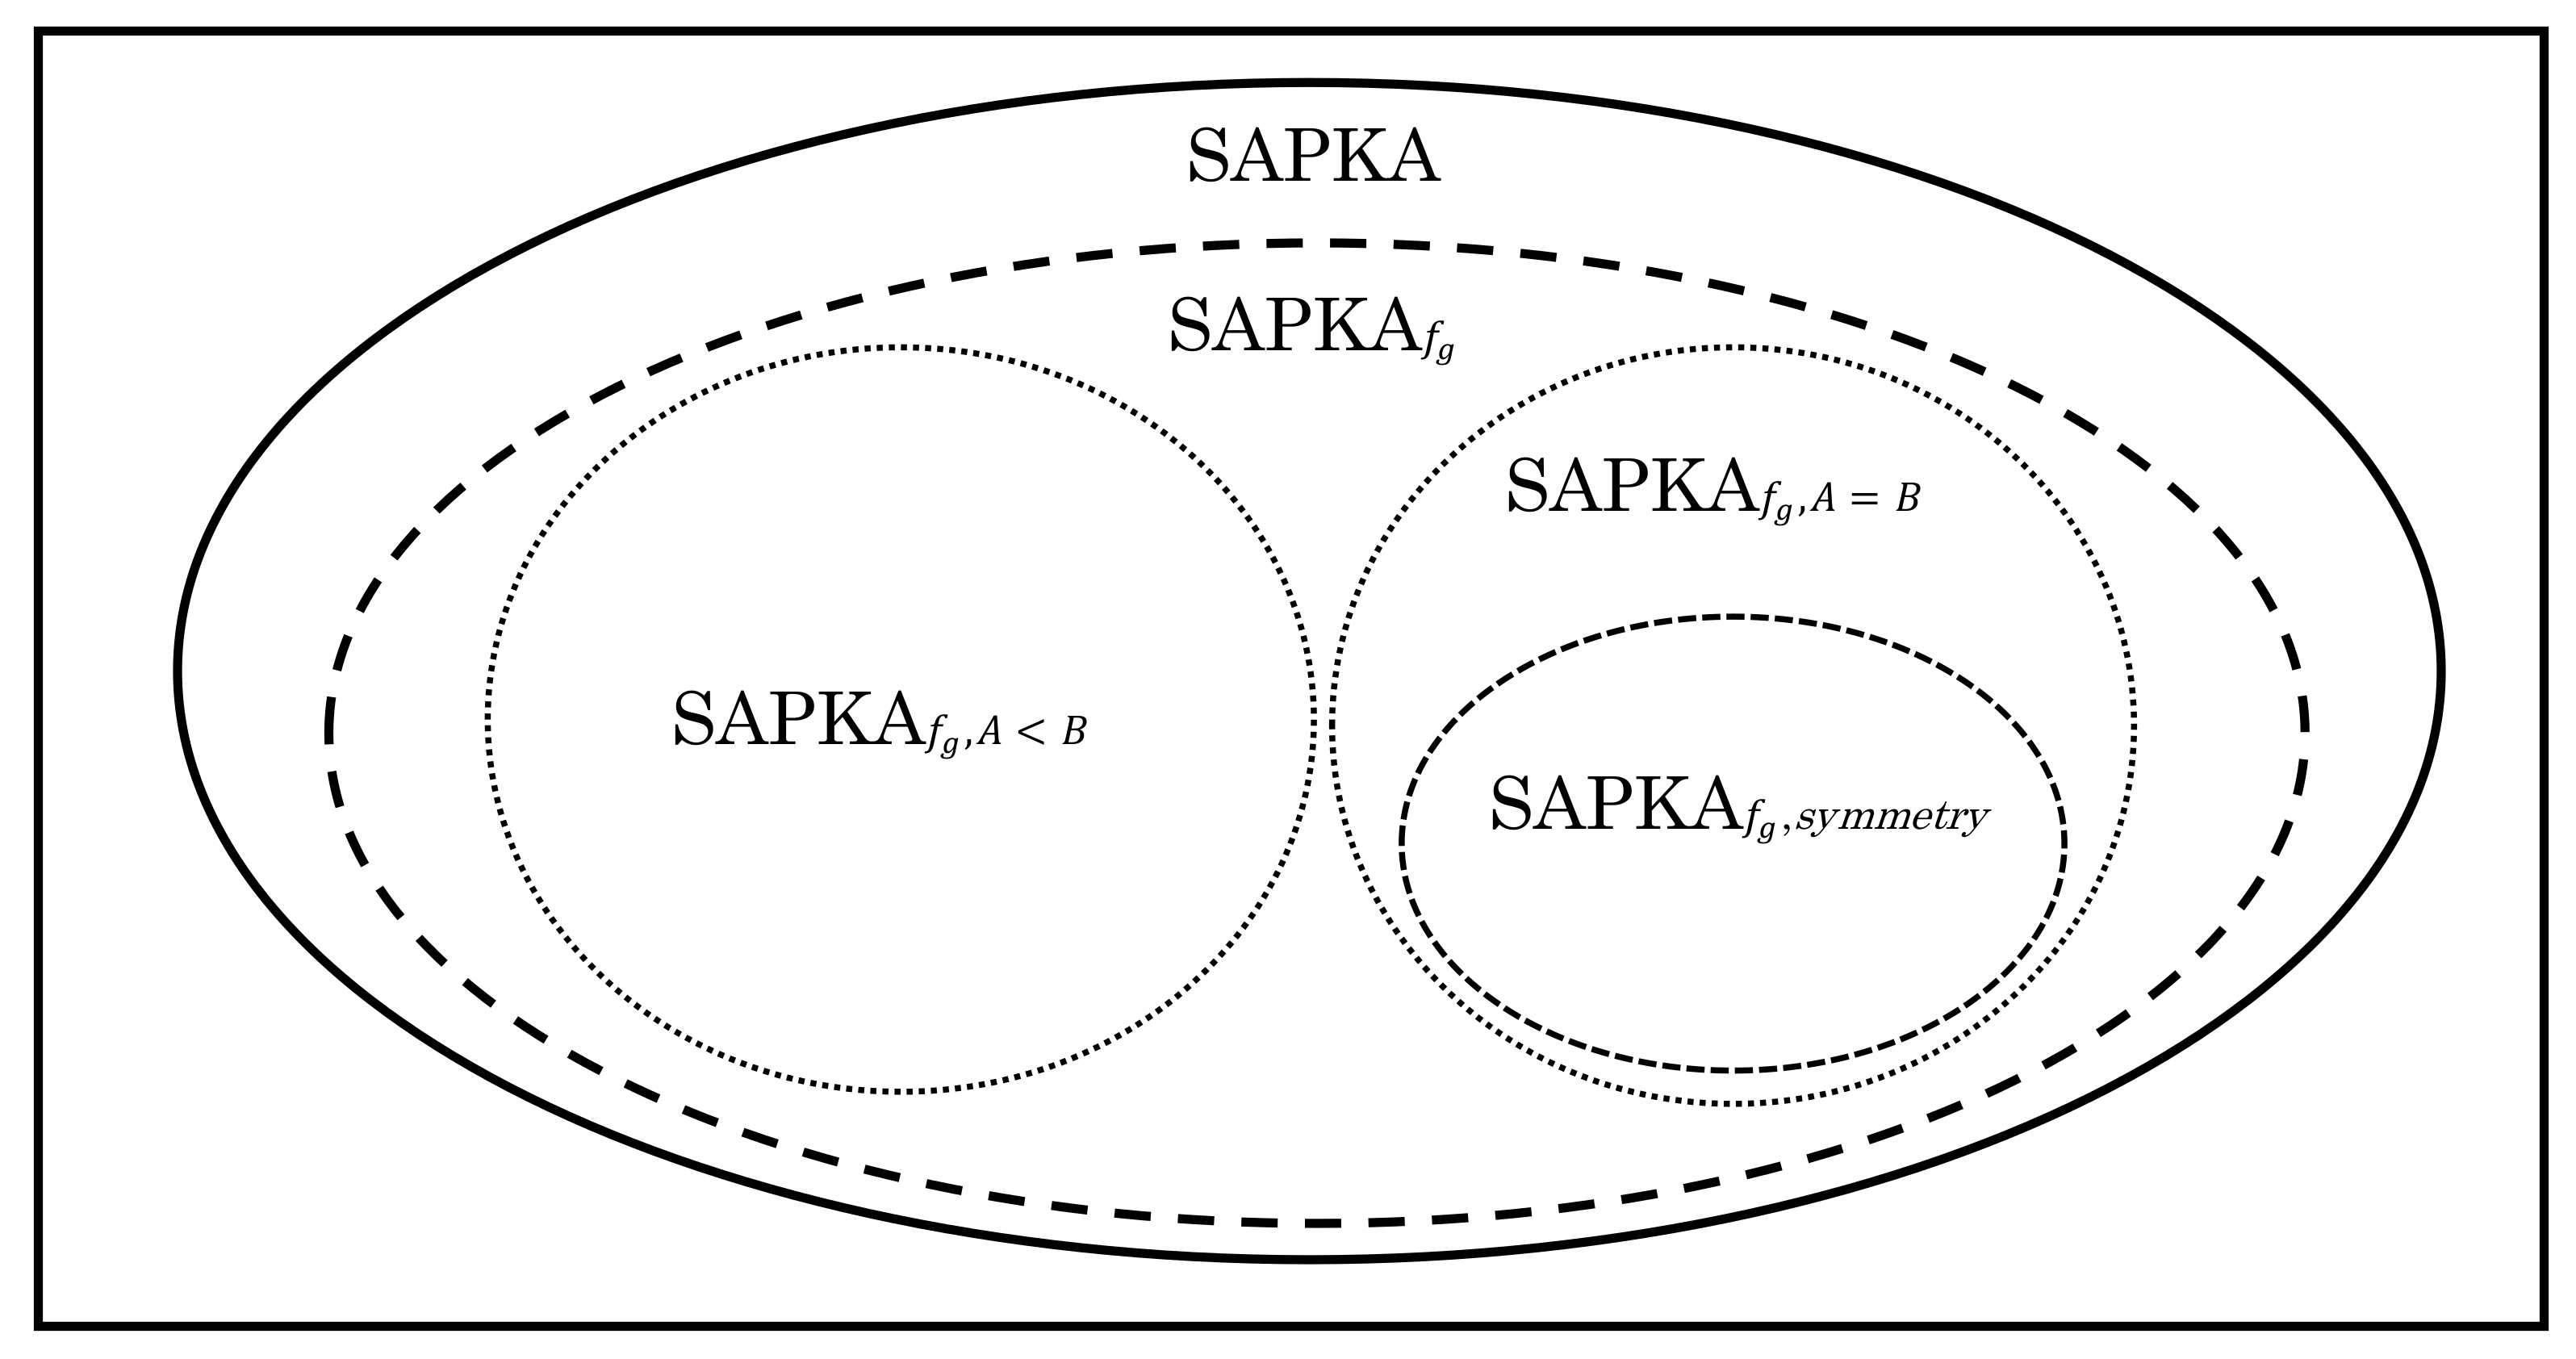
Figure 3 presents the inclusion relations between the subclasses of SAPKA.
Figure 3.
Inclusion relations between subclasses of SAPKA.
6. Implementational Experiments
In this section, we report the simple experimental results. All experiments were performed in the following environment:
- OS: Windows 10 Pro
- Processor: 2.90 GHz Intel Core i7-10700
- RAM: 8 GB
- Language: JAVA
Table 7, Table 8 and Table 9 indicate the computational complexity for Alice () and Bob () according to d and m while n was fixed as 1024, 3072, and 5120 bits. As can be observed from Table 7, Table 8 and Table 9, the calculation time for Bob increased as d increased. This is because the calculation complexities of (32) and (33) were dependent only on d, whereas n was fixed. For Alice’s computation, there were cases in which the calculation time decreased as d increased (Table 8 and Table 9). This can be explained by (32) and (33) for each , being independent, and an increase in d resulted in a decrease in m. Therefore, these values can be computed in parallel with a smaller m when d increases. When , the calculation time will increase despite the decrease in the size of m owing to a shortage in processors for efficient parallel computing.
Table 7.
Calculation time (ms) for Alice and Bob when .
Table 8.
Calculation times (ms) for Alice and Bob when .
Table 9.
Calculation times (ms) for Alice and Bob when .
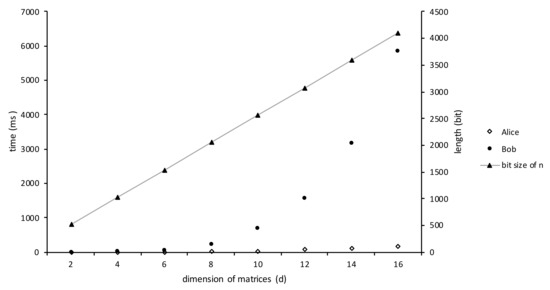
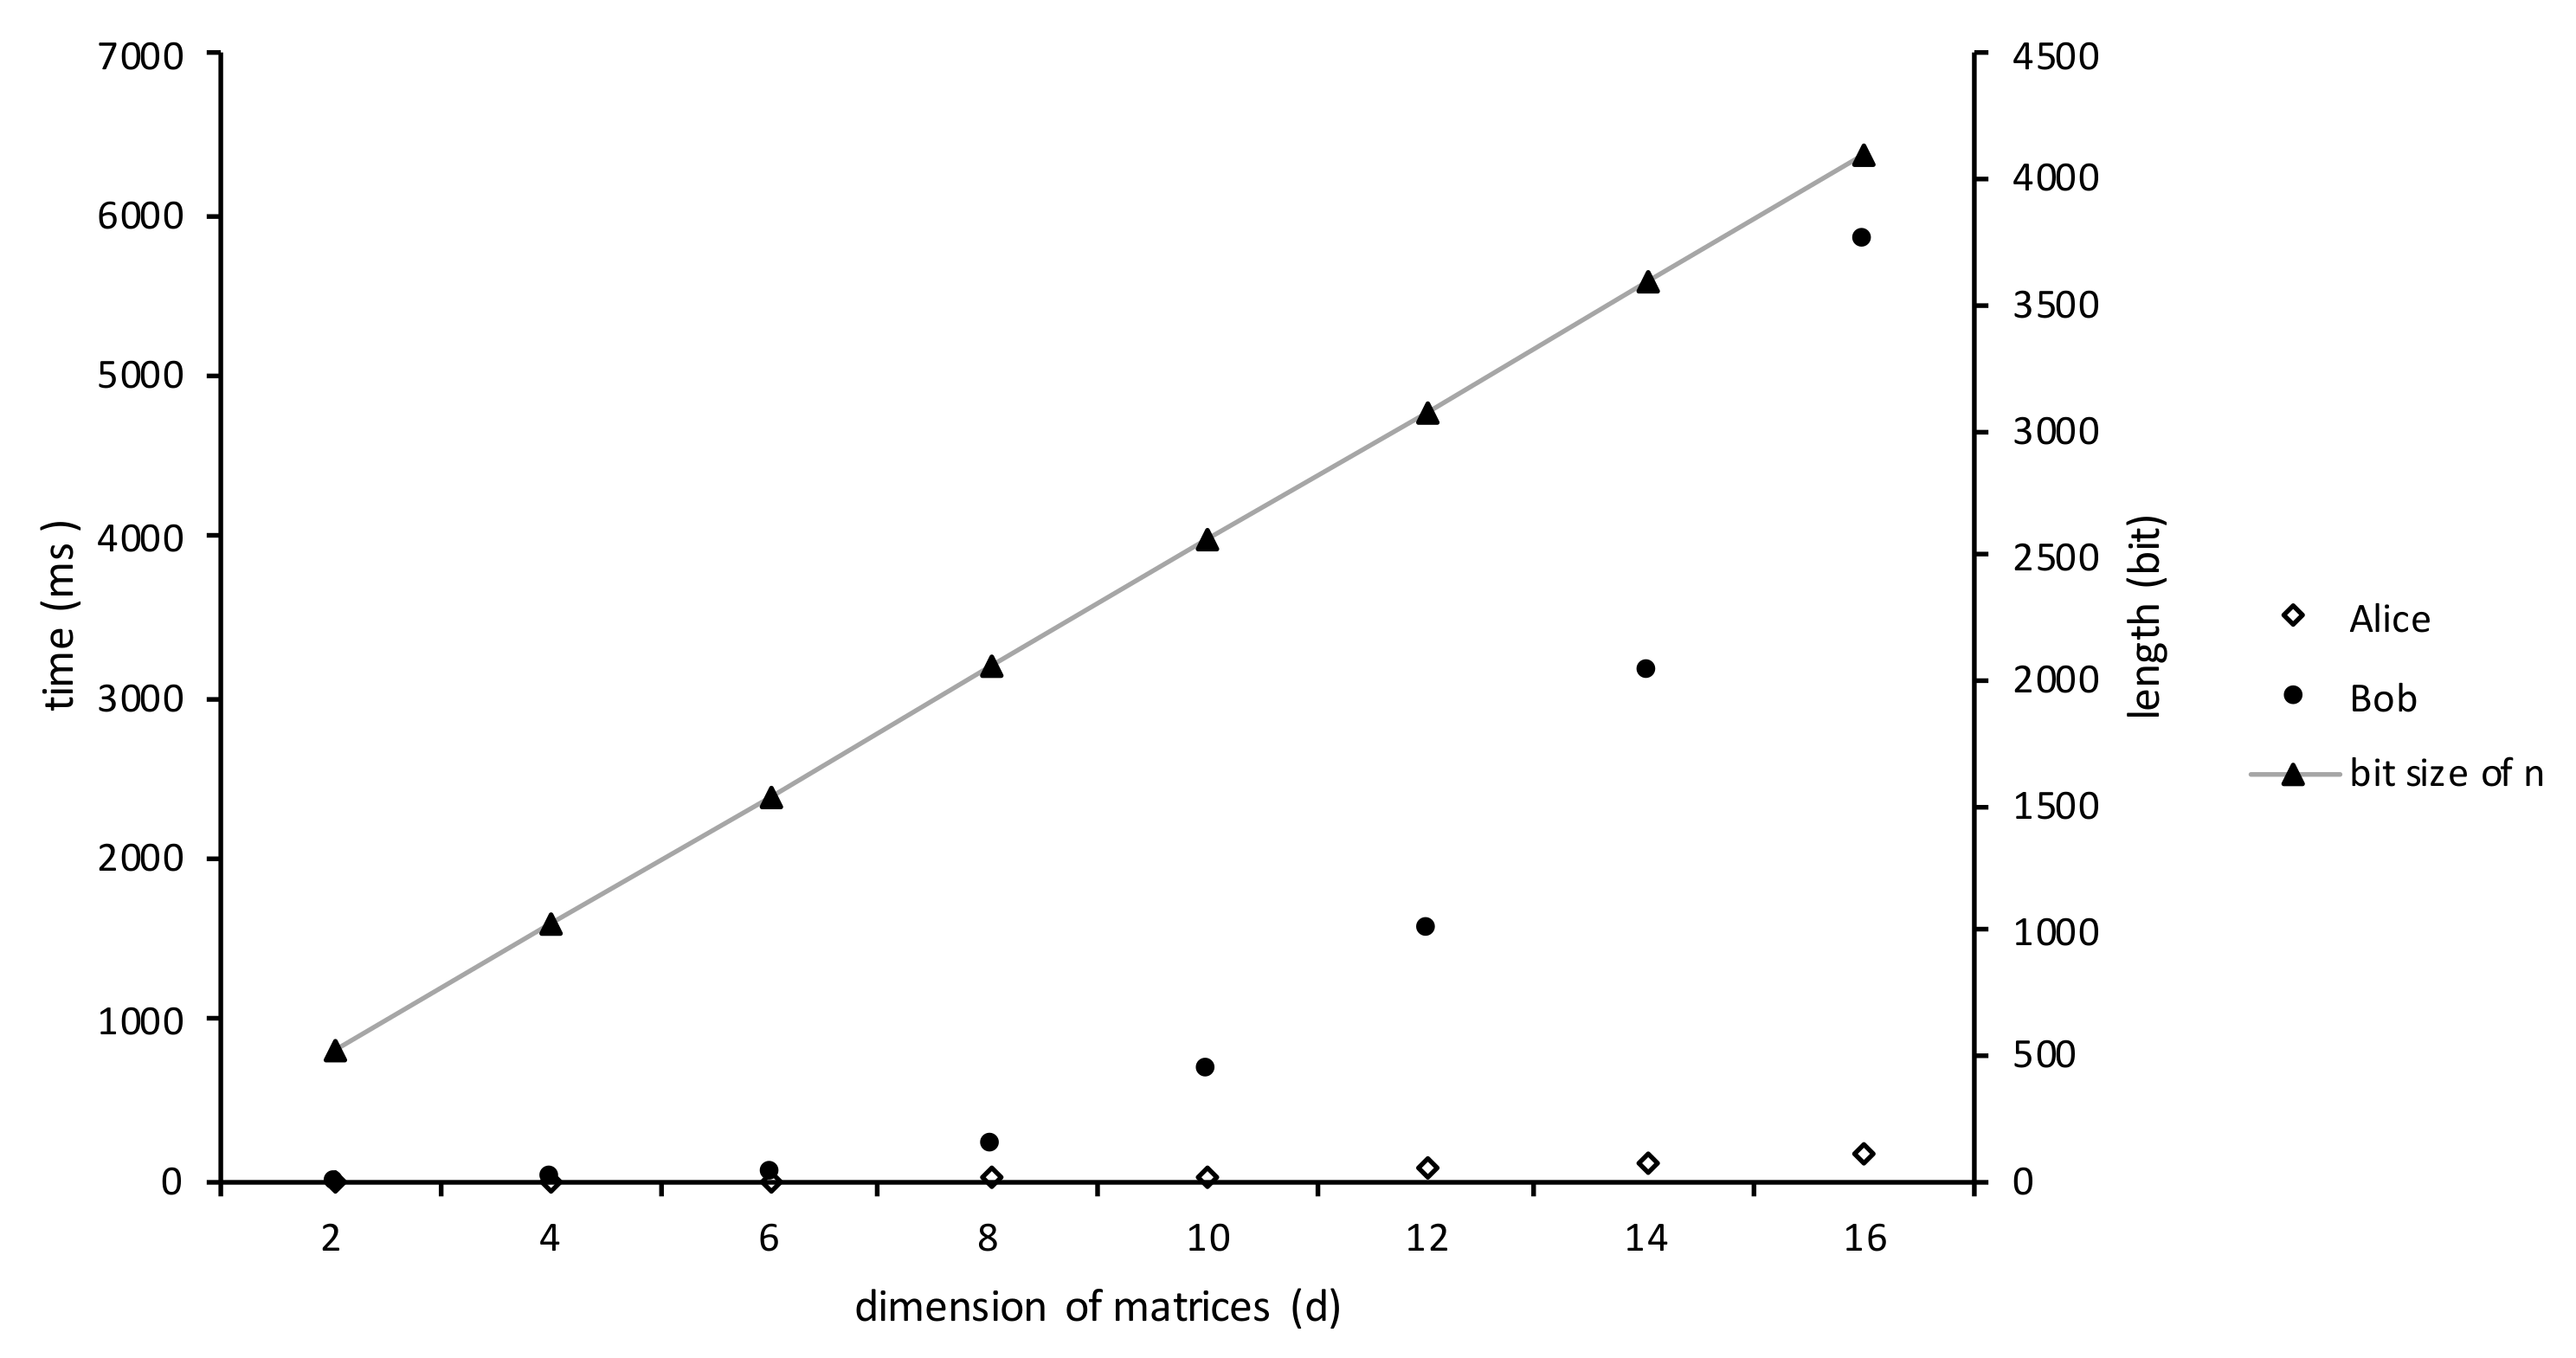
Moreover, the difference in the order of complexity for Alice and Bob can be observed from Figure 4, where m was fixed as 128 bits and d increased from 2 to 16.
Figure 4.
Comparison of calculation times (ms) for Alice and Bob according to d (m = 128).
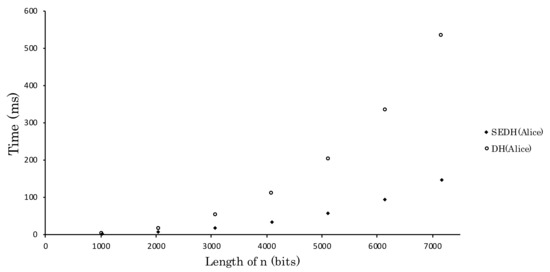
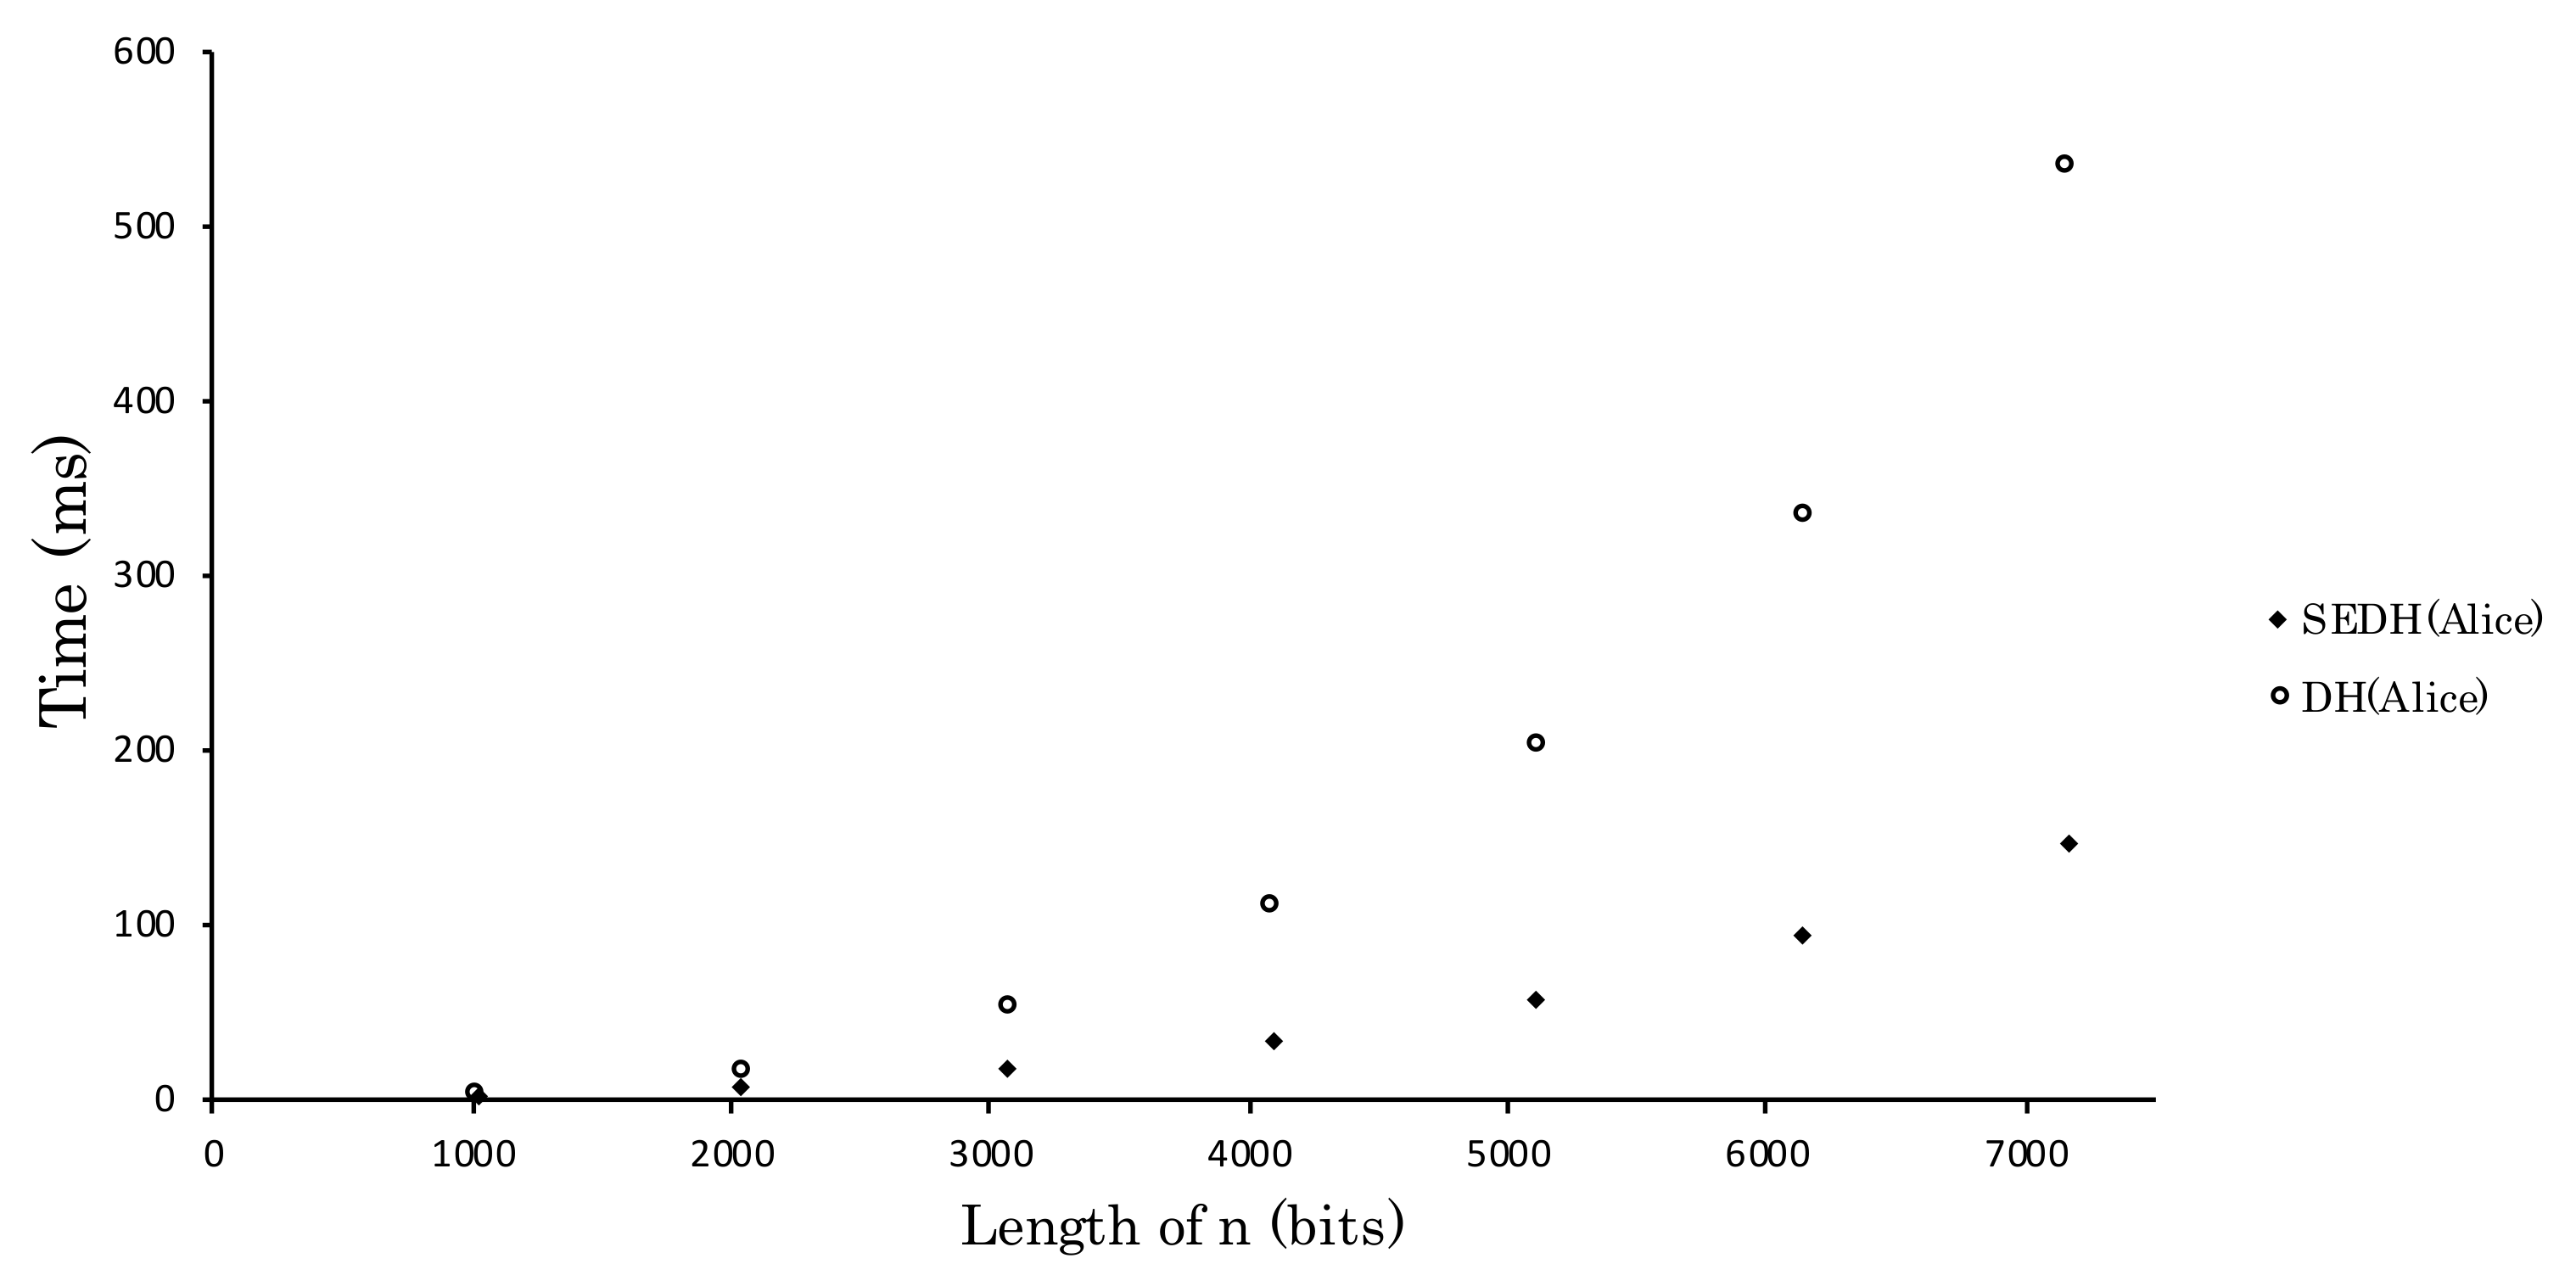
We verified how rapidly the calculation of Alice could be achieved by comparing the speed with that of the usual DH. Table 10 and Figure 5 compare the calculation times of SEDH and DH for and for the same security level (n) from 1024 to 7168 bits. The calculation speeds in the following table and figure are the averages of 50 calculations.
Table 10.
Comparison of calculation times (ms) for Alice with DH.
Figure 5.
Comparison of calculation times (ms) for Alice with DH.
7. Conclusions
In this study, we have estimated the breaking complexity and computational complexity of two SAPKA class algorithms. One of these potentially possesses the property whereby the security is less dependent on the secret key space of Alice than that of Bob. This property allows Alice to calculate her SSK with less complexity than Bob in the algorithm.
Moreover, we generalized these algorithms and constructed SAPKA subclasses according to the security/efficiency properties. We constructed several subclass algorithms in which the above property holds. We expect that algorithms in this class will aid in constructing secure communication infrastructures, even with a small capability of devices for one side (Alice’s computational asymmetry). The necessary conditions for this class and inclusion relations with other SAPKA subclasses were also investigated.
In the following Future Work section, we provide several unclear points, which include new problems obtained from this study (indicated by •) and problems not discussed in this paper but that must be investigated for practical use of presented algorithms and frameworks (indicated by ∘).
Future Works
- ●
- Is it true that ? (Remark 5)
- ●
- Is it true that if the relations (52) and (53) hold for , C is a member of the class? That is, are (52) and (53) also sufficient conditions for the class? As mentioned in Section 2.2, this paper does not provide how to construct secure PKA algorithms resilient to any types of theoretical attacks. However, if sufficient conditions for the class are found, algorithms that cannot be broken at least within polynomial time can be easily constructed because those are protected thanks to non-easily mappable (page 23). Of course, conditions might differ depending on required security level, but considering the sufficient conditions surely helps us provide how to construct secure PKA algorithms.
- ●
- Does need to be selected as a multiplicative semi-group/group? For example, the algorithms in Section 3.3 are effective even in vector space, which forms an additive group (Remark 1). We should investigate how we can construct PKA algorithms on algebraic structures other than multiplicative semi-groups and then compare the breaking and computational complexities with the original one.
- ∘
- We should attempt to describe algorithms such as LWE-based or NTRU-type algorithms with the SAPKA parameters and verify whether these algorithms belong to the class. Otherwise, would it be possible to modify these to belong to the class?
- ∘
- It is well known that key agreement algorithms are vulnerable against man-in-the-middle (MITM) attack. Obviously, also algorithms in SAPKA are also not exceptional without any measures. Moreover, the number of public keys especially for Bob is larger than symmetric type algorithms, so they way to manage public keys for SAPKA algorithms must be discussed more. Adaptability with techniques such as digital signature [21,22] and public key certifications [23] must be well discussed.
- ∘
- As mentioned in [1], the SSKs that Alice and Bob calculate should be ephemeral, and each key must have enough randomness. To practically use algorithms introduced in this paper, if public keys and SSK are sufficiently random to protect Eve from deducing SSK must be investigated.
Author Contributions
Conceptualization, K.J., S.I. and M.R.; Formal analysis, K.J. and S.I.; Implementation, K.J.; Writing—original draft, K.J.; Writing—review and editing, K.J., S.I. and M.R. All authors have read and agreed to the published version of the manuscript.
Funding
This research received no external funding.
Institutional Review Board Statement
Not applicable.
Informed Consent Statement
Not applicable.
Conflicts of Interest
The authors declare no conflict of interest.
Abbreviations
The following abbreviations are used in this manuscript:
| PKA | public key agreement |
| SAPKA | strongly asymmetric public key agreement |
| SSK | secret shared key |
| DH | Diffie-Hellman |
| NDH | Noised Diffie-Hellman |
| SEDH | Schur Exponentiation-Based Diffie-Hellman |
| DLP | discrete logarithm problem |
| MITM | man-in-the-middle |
References
- Shannon, C.E. Communication Theory of Secrecy Systems. Bell Syst. Tech. J. 1949, 28, 656–715. [Google Scholar] [CrossRef] [Scilit]
- Diffie, W.; Hellman, M. New directions in cryptography. IEEE Trans. Inf. Theory 1976, 22, 644–654. [Google Scholar] [CrossRef] [Scilit]
- Rivest, R.L.; Shamir, A.; Adleman, L. A method for obtaining digital signatures and public-key cryptosystems. Commun. ACM 1978, 21, 120–126. [Google Scholar] [CrossRef] [Scilit]
- Adrian, D.; Bhargavan, K.; Durumeric, Z.; Gaudry, P.; Green, M.; Halderman, J.A.; Heninger, N.; Springall, D.; Thomé, E.; Valenta, L.; et al. Imperfect Forward Secrecy: How Diffie-Hellman Fails in Practice. In Proceedings of the 22nd ACM SIGSAC Conference on Computer and Communications Security, Denver, CO, USA, 12–16 October 2015; pp. 5–17. [Google Scholar]
- Shor, P.W. Polynomial-Time Algorithms for Prime Factorization and Discrete Logarithms on a Quantum Computer. SIAM J. Comput. 1997, 26, 1484–1509. [Google Scholar] [CrossRef] [Scilit]
- Bernstein, D.J.; Chuengsatiansup, C.; Lange, T.; van Vredendaal, C. NTRU Prime: Reducing Attack Surface at Low Cost. In Selected Areas in Cryptography—SAC 2017; Lecture Notes in Computer Science; Adams, C., Camenisch, J., Eds.; Springer: Cham, Switzerland, 2017; Volume 10719. [Google Scholar] [CrossRef] [Scilit]
- Hülsing, A.; Rijneveld, J.; Schanck, J.; Schwabe, P. High-Speed Key Encapsulation from NTRU. In Cryptographic Hardware and Embedded Systems—CHES 2017; Lecture Notes in Computer Science; Fischer, W., Homma, N., Eds.; Springer: Cham, Switzerland, 2017; Volume 10529. [Google Scholar] [CrossRef] [Scilit]
- Hoffstein, J.; Pipher, J.; Silverman, J.H. NTRU: A ring-based public key cryptosystem. In Algorithmic Number Theory—ANTS 1998; Lecture Notes in Computer Science; Buhler, J.P., Ed.; Springer: Berlin/Heidelberg, Germany, 1998; Volume 1423. [Google Scholar] [CrossRef] [Scilit]
- Bos, J.; Ducas, L.; Kiltz, E.; Lepoint, T.; Lyubashevsky, V.; Schanck, J.M.; Schwabe, P.; Seiler, G.; Stehle, D. CRYSTALS—Kyber: A CCA-Secure module-lattice-based KEM. In Proceedings of the 2018 IEEE European Symposium on Security and Privacy (EuroS and P), London, UK, 24–26 April 2018; pp. 353–367. [Google Scholar] [CrossRef] [Scilit]
- Alkim, E.; Ducas, L.; Poppelmann, T.; Schwabe, P. Post-quantum key exchange—A new hope. In Proceedings of the 25th USENIX Security Symposium (USENIX Security 16), Austin, TX, USA, 10–12 August 2016; pp. 327–343. [Google Scholar]
- Post-Quantum Cryptography Competition Round 2 Submissions. Available online: https://csrc.nist.gov/projects/post-quantum-cryptography/round-2-submissions (accessed on 16 March 2021).
- PQC Standardization Process: Third Round Candidate Announcement. Available online: https://csrc.nist.gov/News/2020/pqc-third-round-candidate-announcement (accessed on 16 March 2021).
- Micciancio, D.; Regev, O. Worst-case to average-case reductions based on Gaussian measures. J. Comput. 2007, 37, 267–302. [Google Scholar] [CrossRef] [Scilit]
- Regev, O. On lattices, learning with errors, random linear codes, and cryptography. J. ACM 2009, 56, 1–40. [Google Scholar] [CrossRef] [Scilit]
- Laine, K.; Lauter, K. Key Recovery for LWE in Polynomial Time. IACR Cryptology ePrint Archive 2015, no. 176. Available online: https://eprint.iacr.org/2015/176.pdf (accessed on 14 June 2021).
- Peikert, C. Public-key cryptosystems from the worst-case shortest vector problem. In Proceedings of the forty-first annual ACM symposium on Theory of computing, Bethesda, MD, USA, 31 May–2 June 2009; pp. 333–342. [Google Scholar]
- Coppersmith, D.; Shamir, A. Lattice Attacks on NTRU. In Advances in Cryptology—EUROCRYPT ’97; Lecture Notes in Computer Science; Fumy, W., Ed.; Springer: Berlin, Germany, 1997; Volume 1233. [Google Scholar] [CrossRef] [Scilit]
- Accardi, L.; Iriyama, S.; Regoli, M.; Ohya, M. Strongly Asymmetric Public Key Agreement Algorithms; Technical Report ISEC2011-20; IEICE: Tokyo, Japan, 2011; pp. 115–121. [Google Scholar]
- Pollard, J. Monte Carlo Methods for Index Computation (modp). Math. Comput. 1978, 32, 918–924. [Google Scholar]
- Pohlig, S.; Hellman, M. An improved algorithm for computing logarithms over GF(p) and its cryptographic significance (Corresp.). IEEE Trans. Inf. Theory 1978, 24, 106–110. [Google Scholar] [CrossRef] [Scilit]
- Lamport, L. Constructing Digital Signatures from a One-Way Function; Technical Report CSL-98; SRI International: Menlo Park, CA, USA, 1979; Volume 238. [Google Scholar]
- Merkle, R.C. A Certified Digital Signature, Conference on the Theory and Application of Cryptology; Springer: New York, NY, USA, 1989. [Google Scholar]
- Cooper, D.; Santesson, S.; Farrell, S.; Boeyen, S.; Housley, R.; Polk, W. Internet X. 509 Public Key Infrastructure Certificate and Certificate Revocation List (CRL) Profile, RFC 5280. 2008, pp. 1–151. Available online: https://datatracker.ietf.org/doc/html/rfc5280 (accessed on 14 June 2021).

Publisher’s Note: MDPI stays neutral with regard to jurisdictional claims in published maps and institutional affiliations. |
© 2021 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (https://creativecommons.org/licenses/by/4.0/).