Article

CVMan: A Framework for Clone-Incurred Vulnerability Management

1
National Engineering Research Center for Big Data Technology and System, Services Computing Technology and System Lab, Hubei Engineering Research Center on Big Data Security, School of Cyber Science and Engineering, Huazhong University of Science and Technology, Wuhan 430074, China
2
College of Engineering and Applied Science, University of Colorado Colorado Springs, Colorado Springs, CO 80918, USA
3
National Engineering Research Center for Big Data Technology and System, Services Computing Technology and System Lab, Cluster and Grid Computing Lab, School of Computer Science and Technology, Huazhong University of Science and Technology, Wuhan 430074, China
*
Author to whom correspondence should be addressed.
Appl. Sci. 2023, 13(8), 4948; https://doi.org/10.3390/app13084948
Submission received: 4 March 2023 / Revised: 8 April 2023 / Accepted: 10 April 2023 / Published: 14 April 2023
(This article belongs to the Topic Cyber Security and Critical Infrastructures)

Abstract

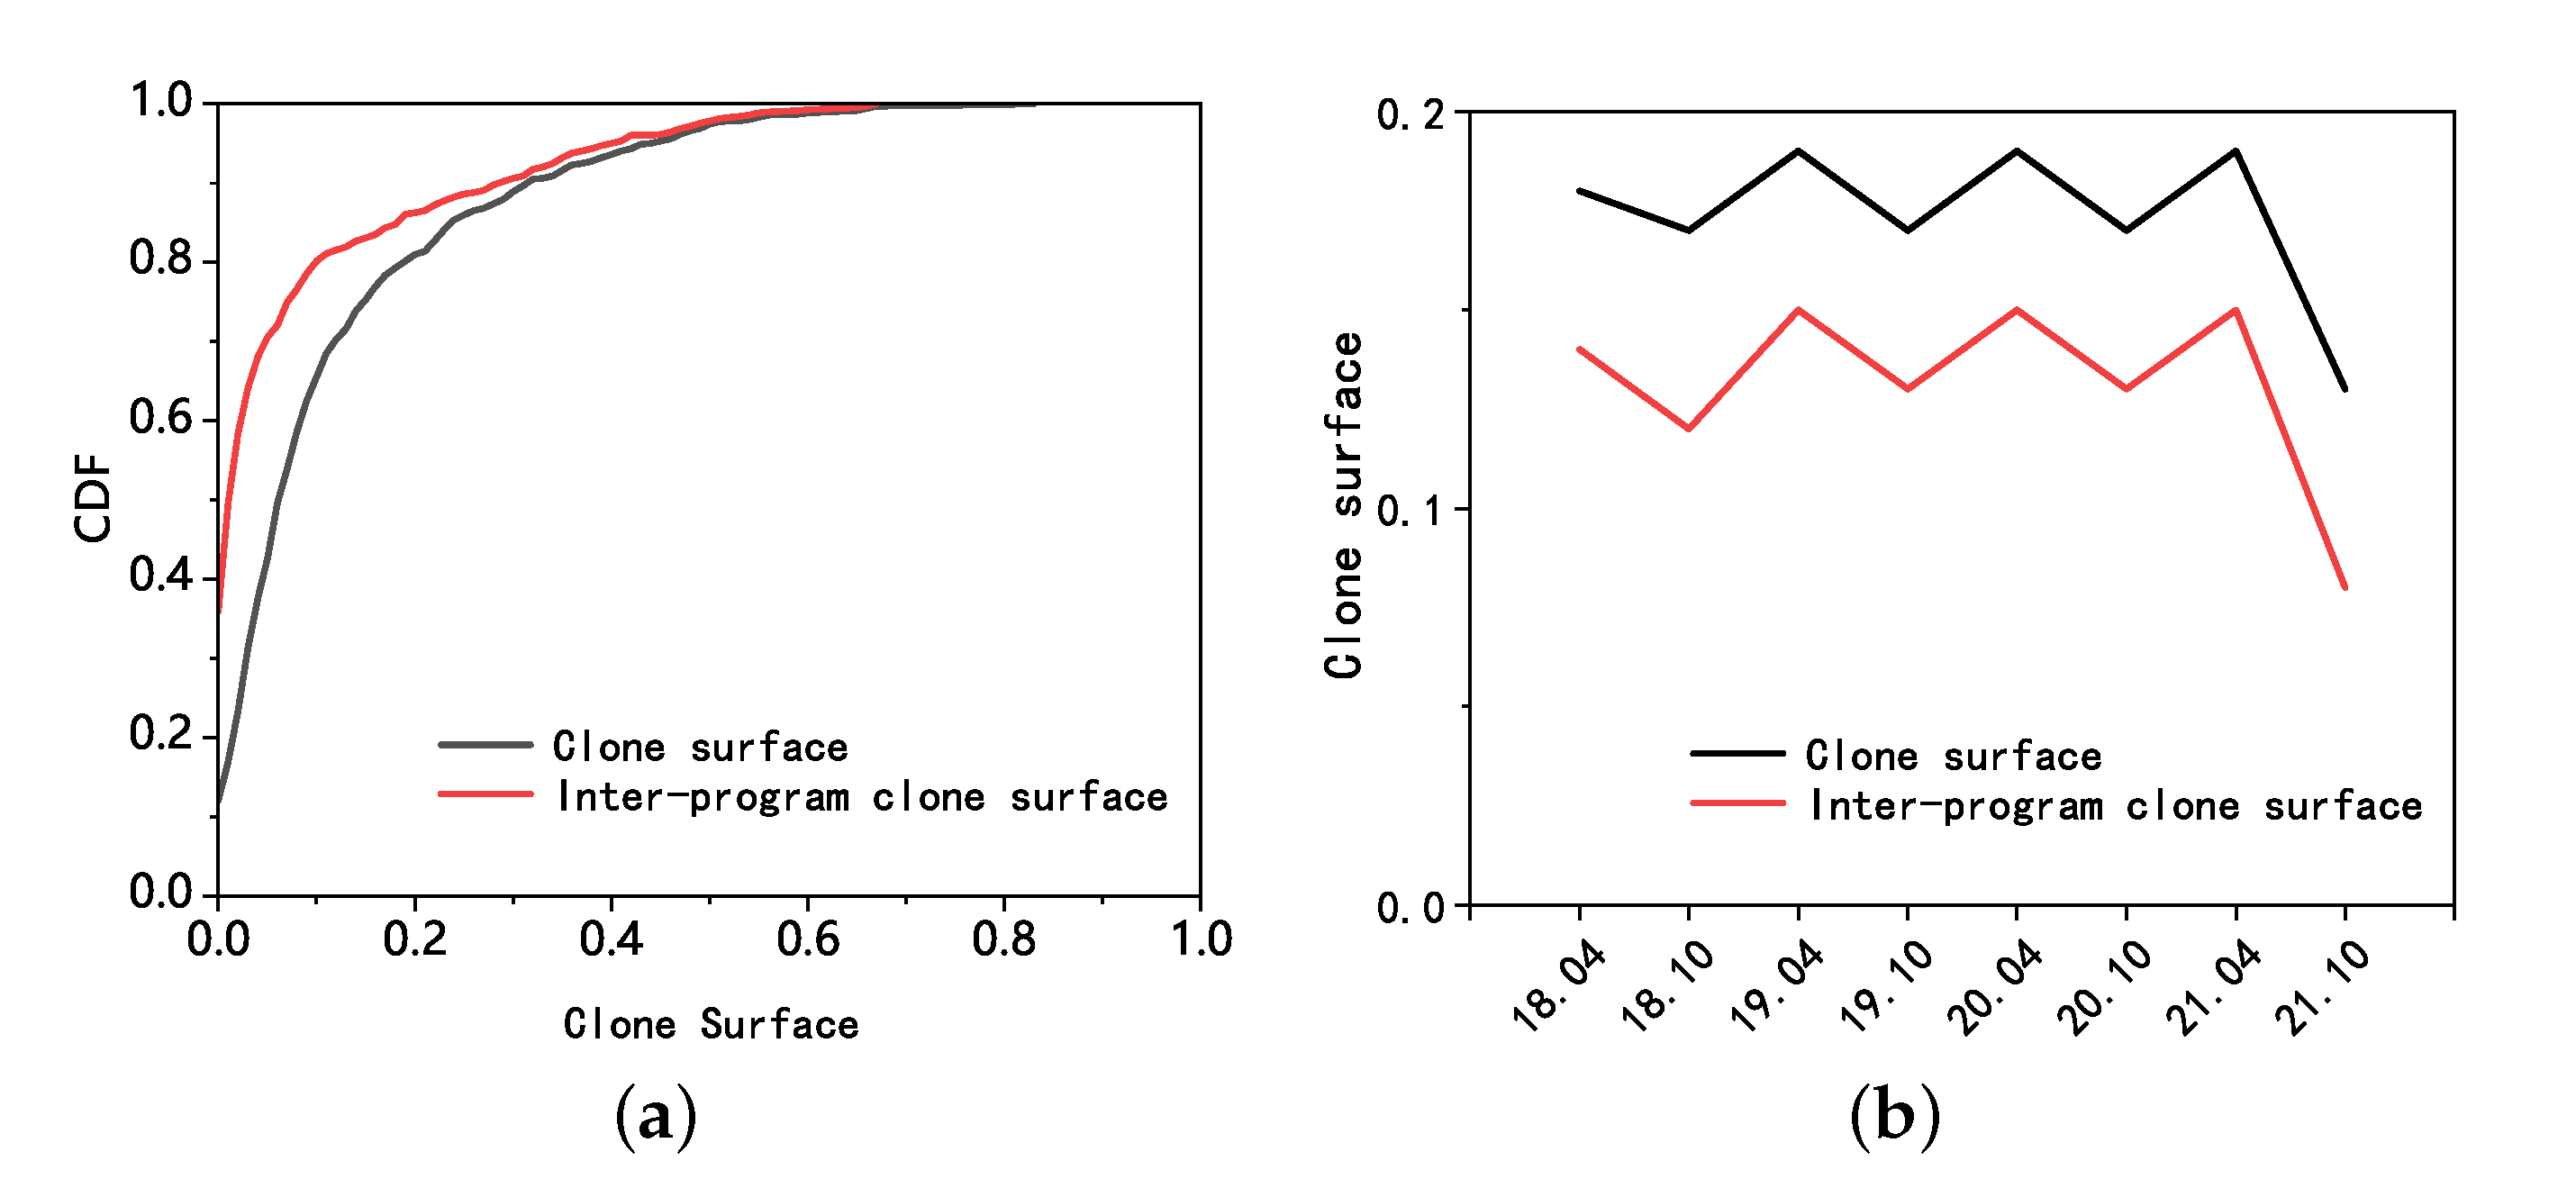
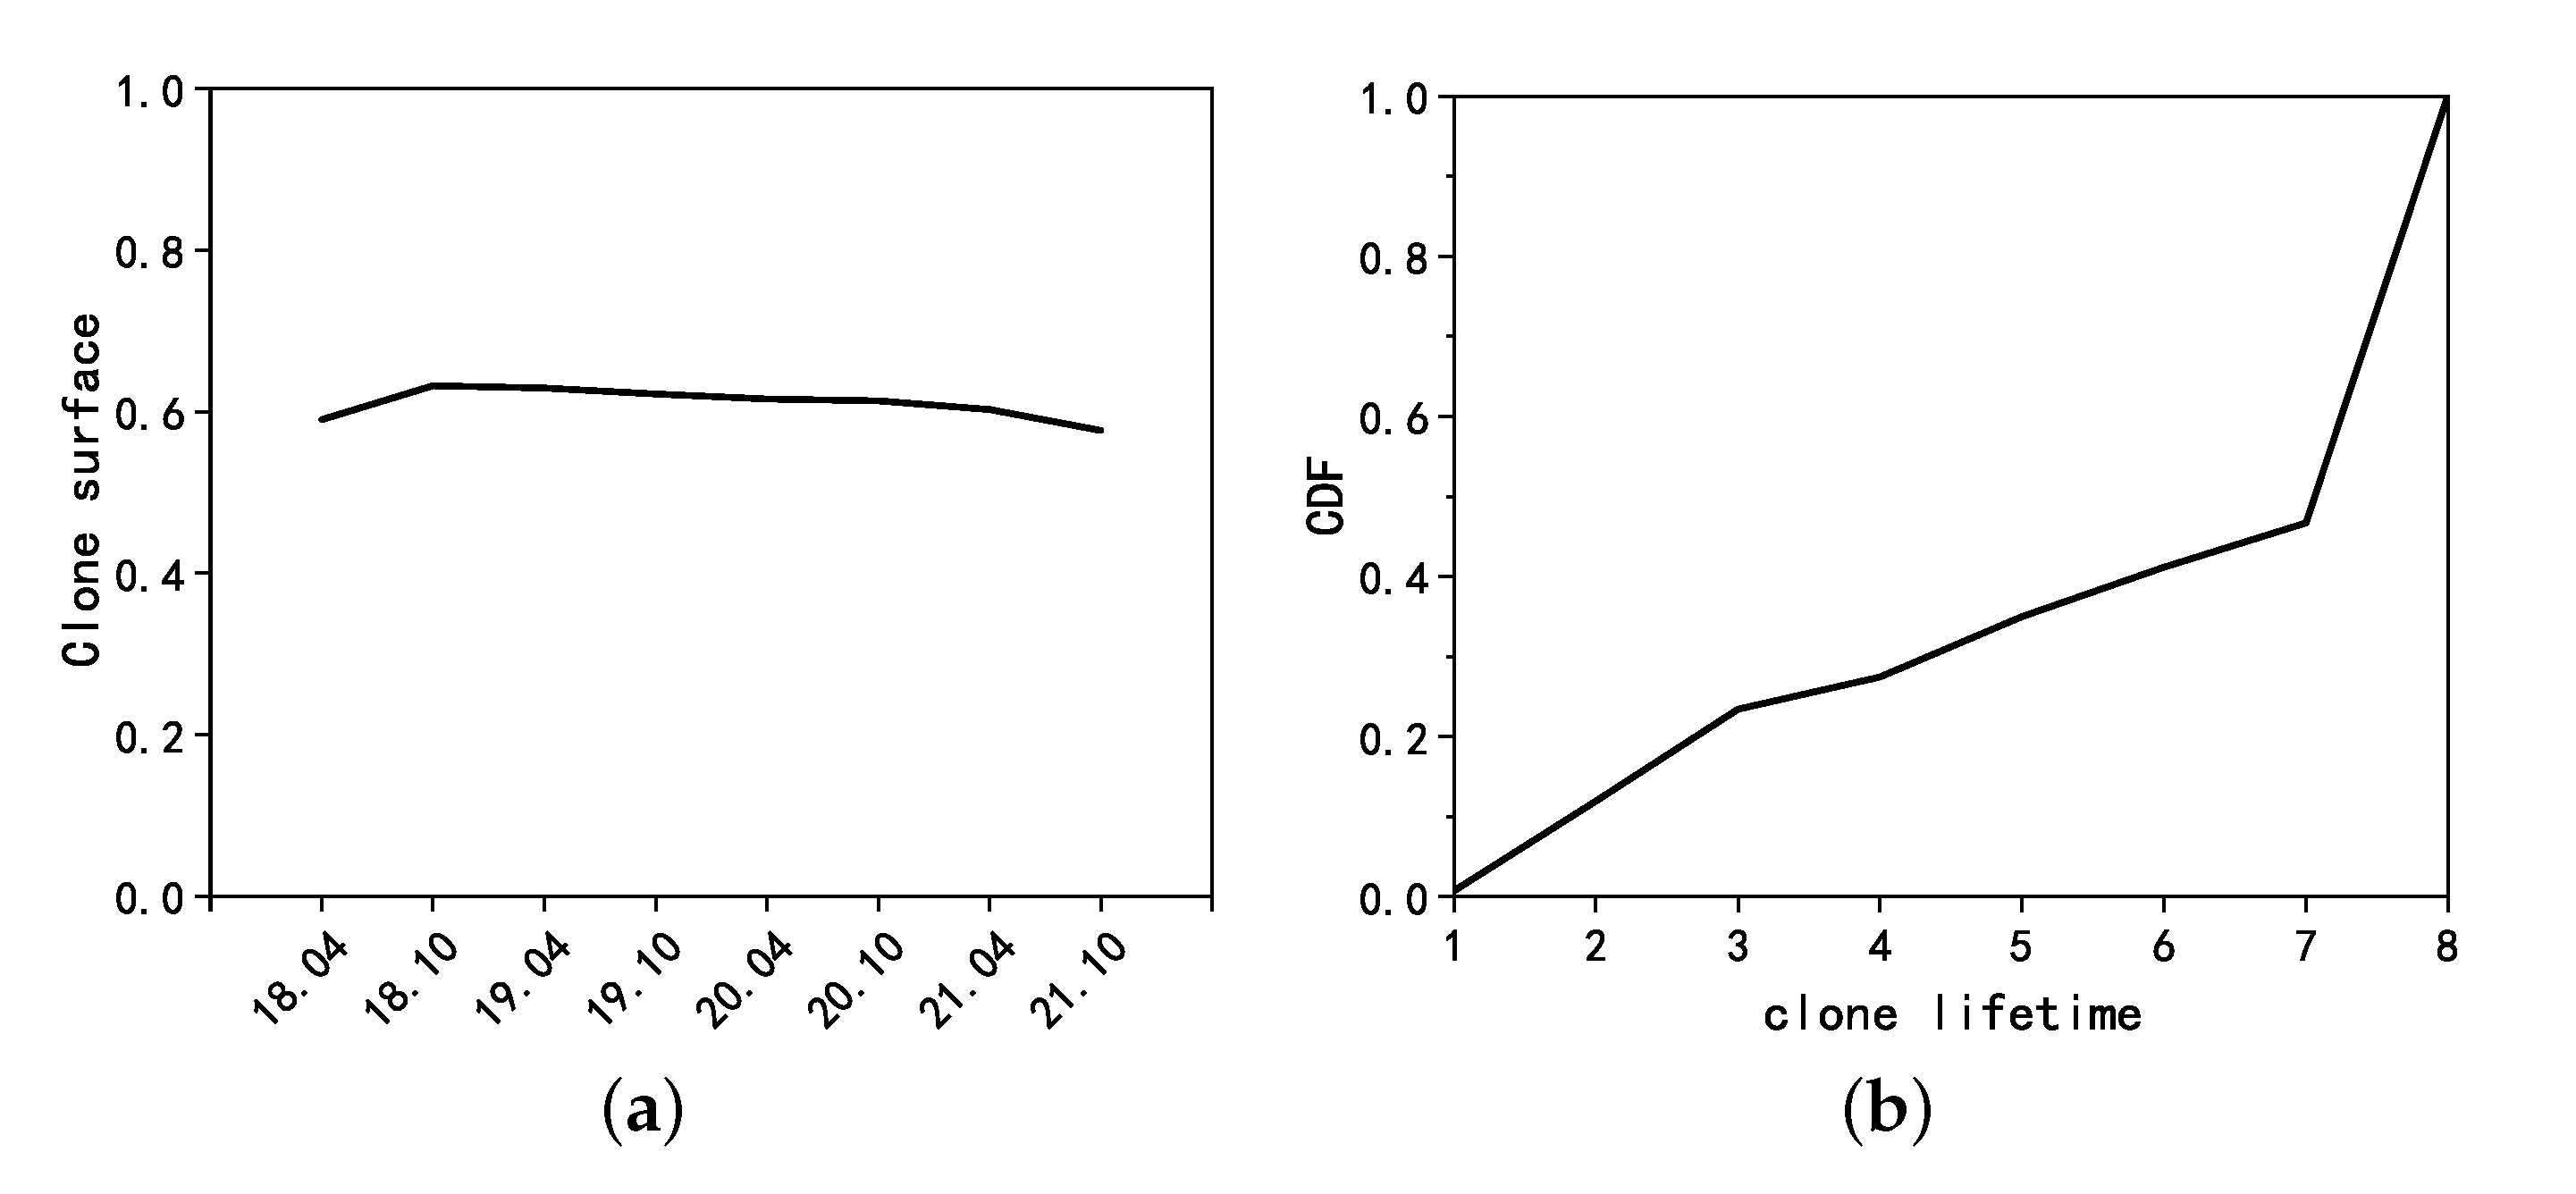
Software clones may cause vulnerability proliferation, which highlights the importance of investigating clone-incurred vulnerabilities. In this paper, we propose a framework for automatically managing clone-incurred vulnerabilities. Two innovations of the framework are the notion of the spatial clone-relation graph, which describes clone-based relationships between software programs, and the temporal clone-relation graph, which describes the evolution of clones in software over time. As a case study, we apply the framework to analyze eight versions of Ubuntu while drawing a number of insights, such as: (i) clones are prevalent with about one-sixth of the codebase being clones; (ii) intra-program clones are often attributed to polymorphisms or functional similarities between procedures, while inter-program clones are often attributed to shared code repositories and the reuse of libraries; (iii) the clone surface of Linux remains stable at around 0.6, meaning that spatial and temporal clones in Linux account for about 60% of the codebase, while the lifetime of 53% clones spans eight versions; and (iv) the clone-incurred vulnerability surface in Linux is small, while vulnerable clones and non-vulnerable clones have similar lifetimes.
Keywords: vulnerability; risk management; clone vulnerability; risk management; clone